Audience: Security Administrators, SOC Analysts, Detection Engineers, MSSPs
Product Module: Securonix SIEM / Microsoft 365 and Entra ID Integration
Last Updated: September 21, 2026
KB ID: KB-20260921-copilot-studio-threat-detection [Tentative]
Tags: Microsoft Copilot Studio, Microsoft Entra ID, Entra Agent ID, OAuth, Microsoft Purview, Power Platform, CopilotInteraction, threat detection, Office 365, Securonix SIEM
Problem
Copilot Studio introduces new security risks across agent creation, identity provisioning, OAuth permissions, user interactions, and access to sensitive enterprise data.
Because agent activity spans multiple Microsoft services, security teams cannot rely on a single log source to identify suspicious behavior. Effective monitoring requires visibility across Power Platform, Microsoft Entra ID, Copilot interaction telemetry, Application Insights, and DLP and data-access logs.
Objective
This article explains the identity lifecycle, OAuth permission model, and logging architecture of Microsoft Copilot Studio agents. It also outlines how security teams can correlate these signals in Securonix SIEM to identify suspicious agent creation, permission changes, Copilot interactions, sensitive resource access, and potential data movement.
Introduction
As organizations rapidly adopt Microsoft Copilot Studio to build AI-powered agents, security teams are faced with a new challenge:
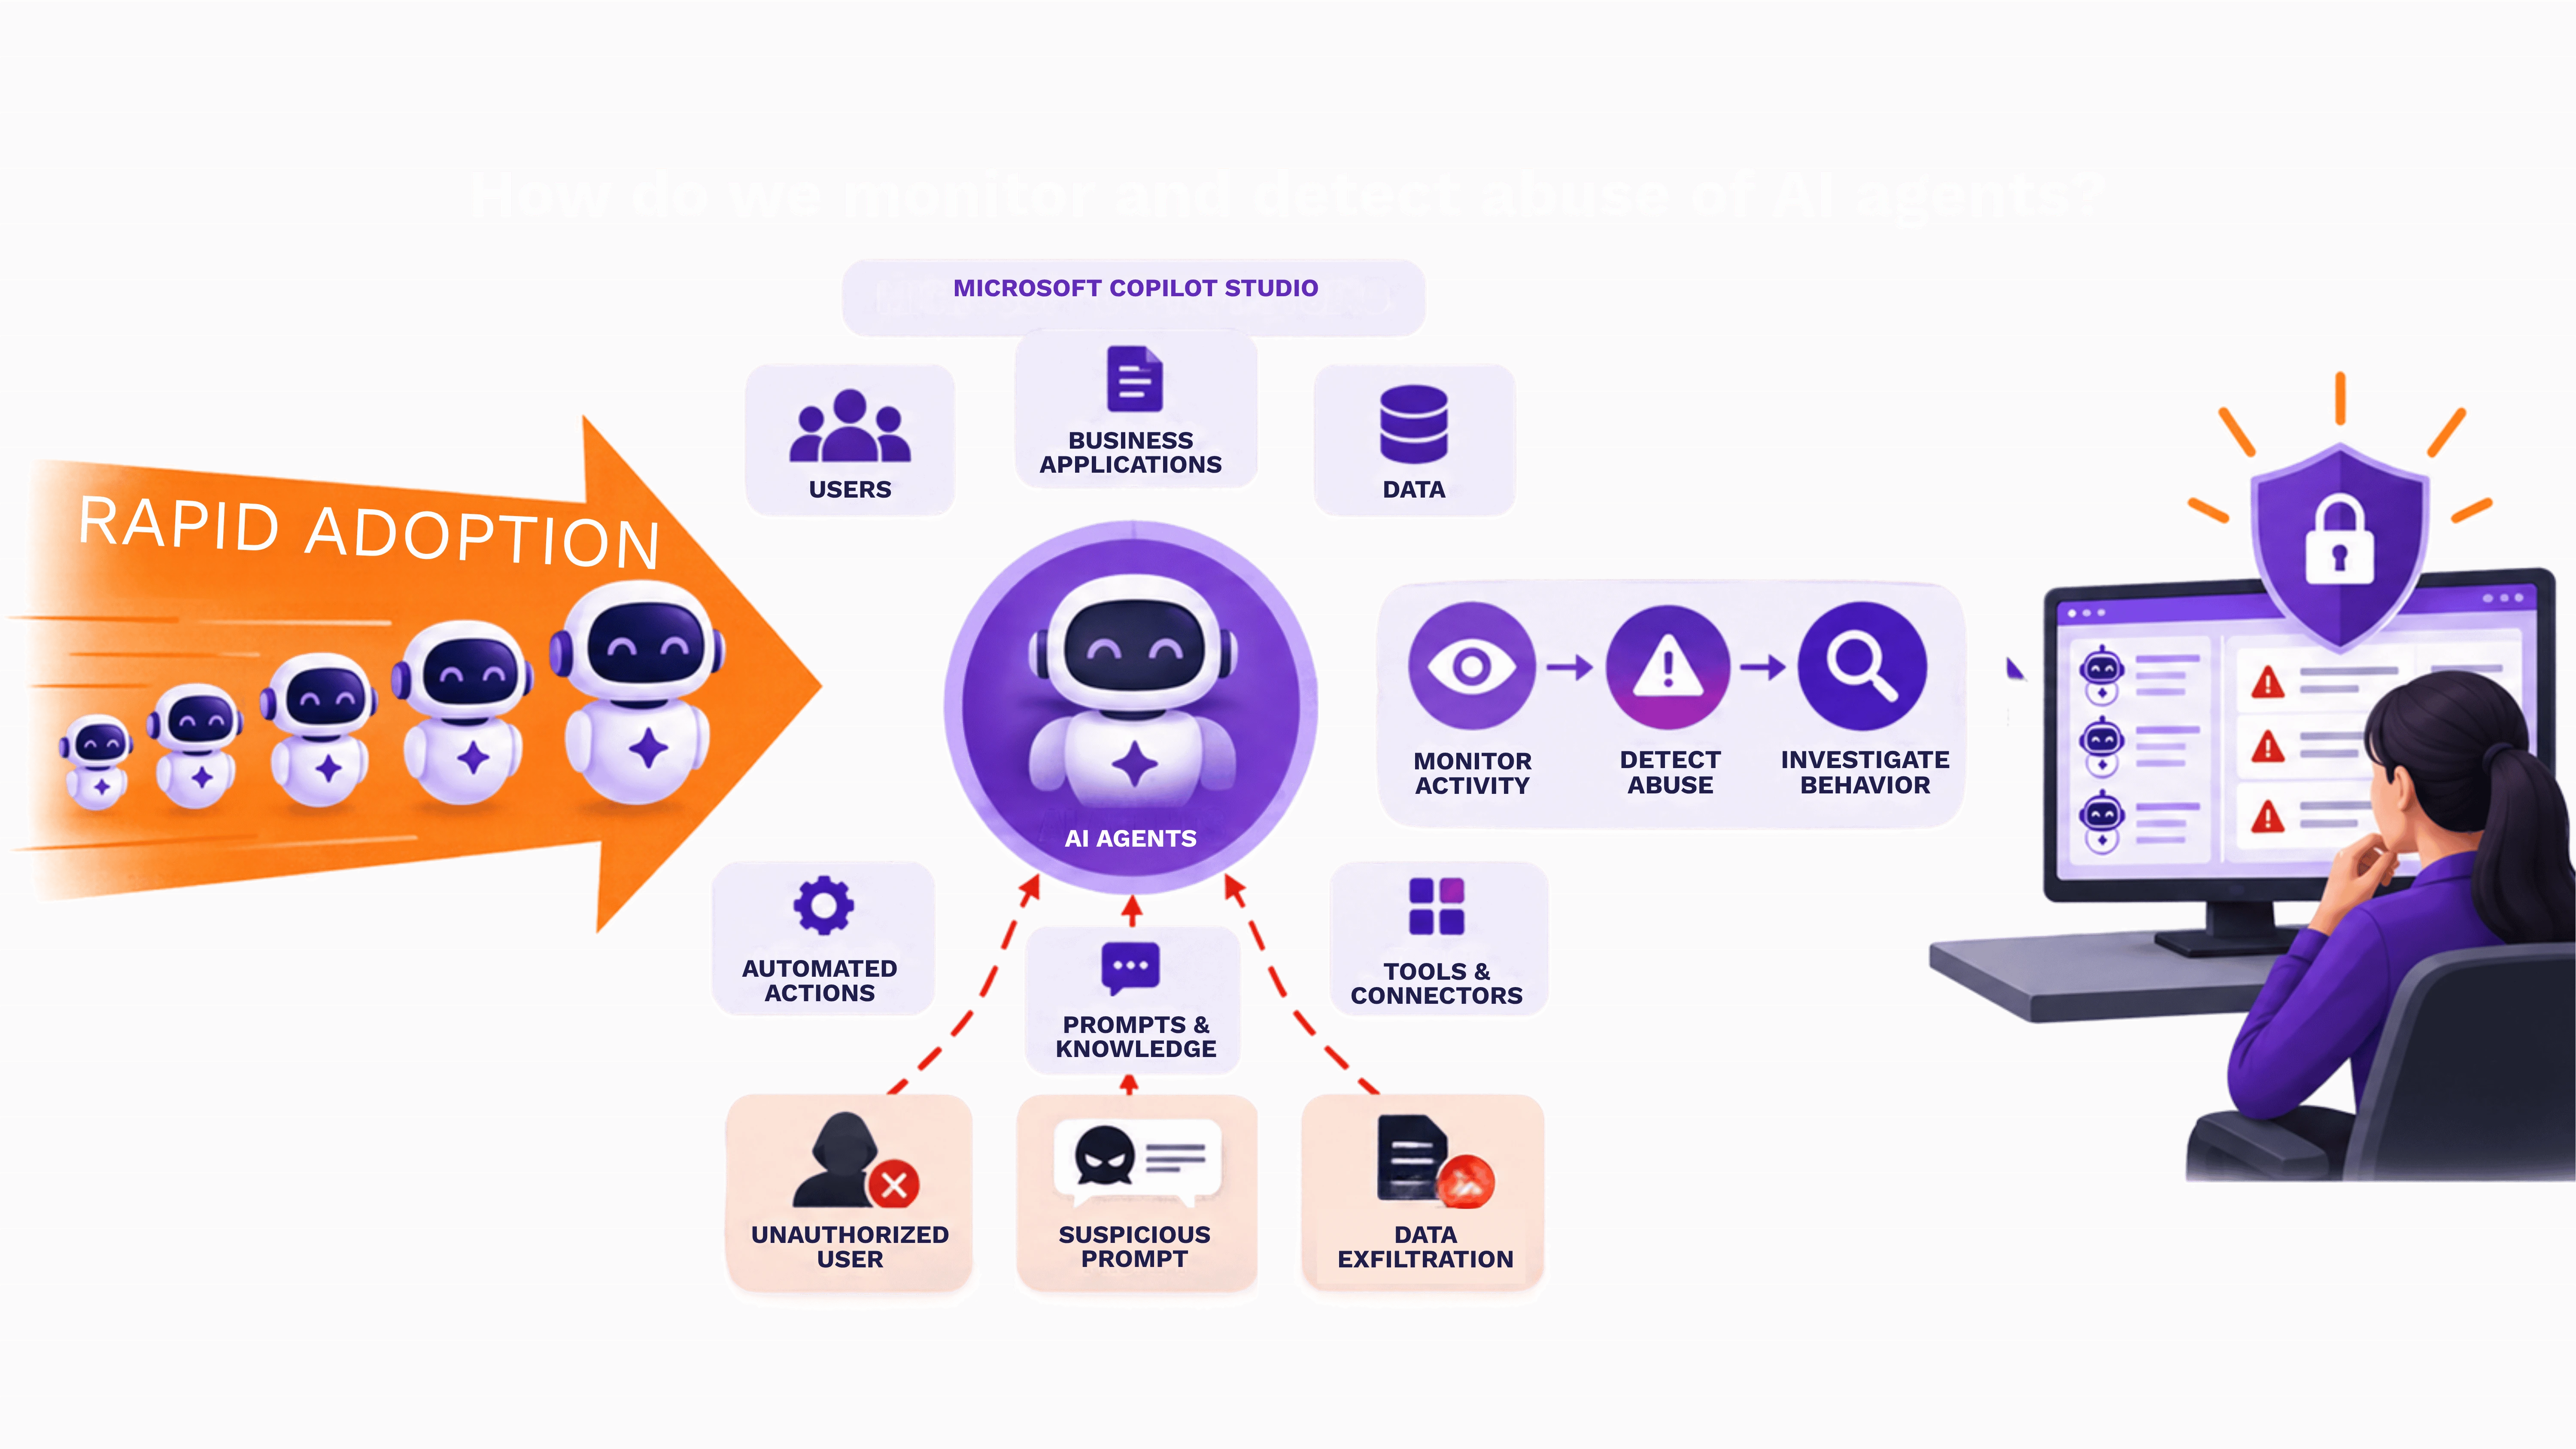
Unlike traditional applications, Copilot Studio automatically provisions Microsoft Entra applications and Identities, relies on delegated OAuth permissions to access Microsoft 365 resources, and generates telemetry across multiple Microsoft services. Understanding how these pieces fit together is essential for building effective detections.
This article summarizes the identity lifecycle of a Copilot Studio agent, explains where logs are generated, and outlines the most valuable threat detection opportunities.
Copilot Studio Architecture:
Copilot Studio is built on top of the Power Platform, but its security model extends well beyond it.
An agent interacts with several Microsoft services:
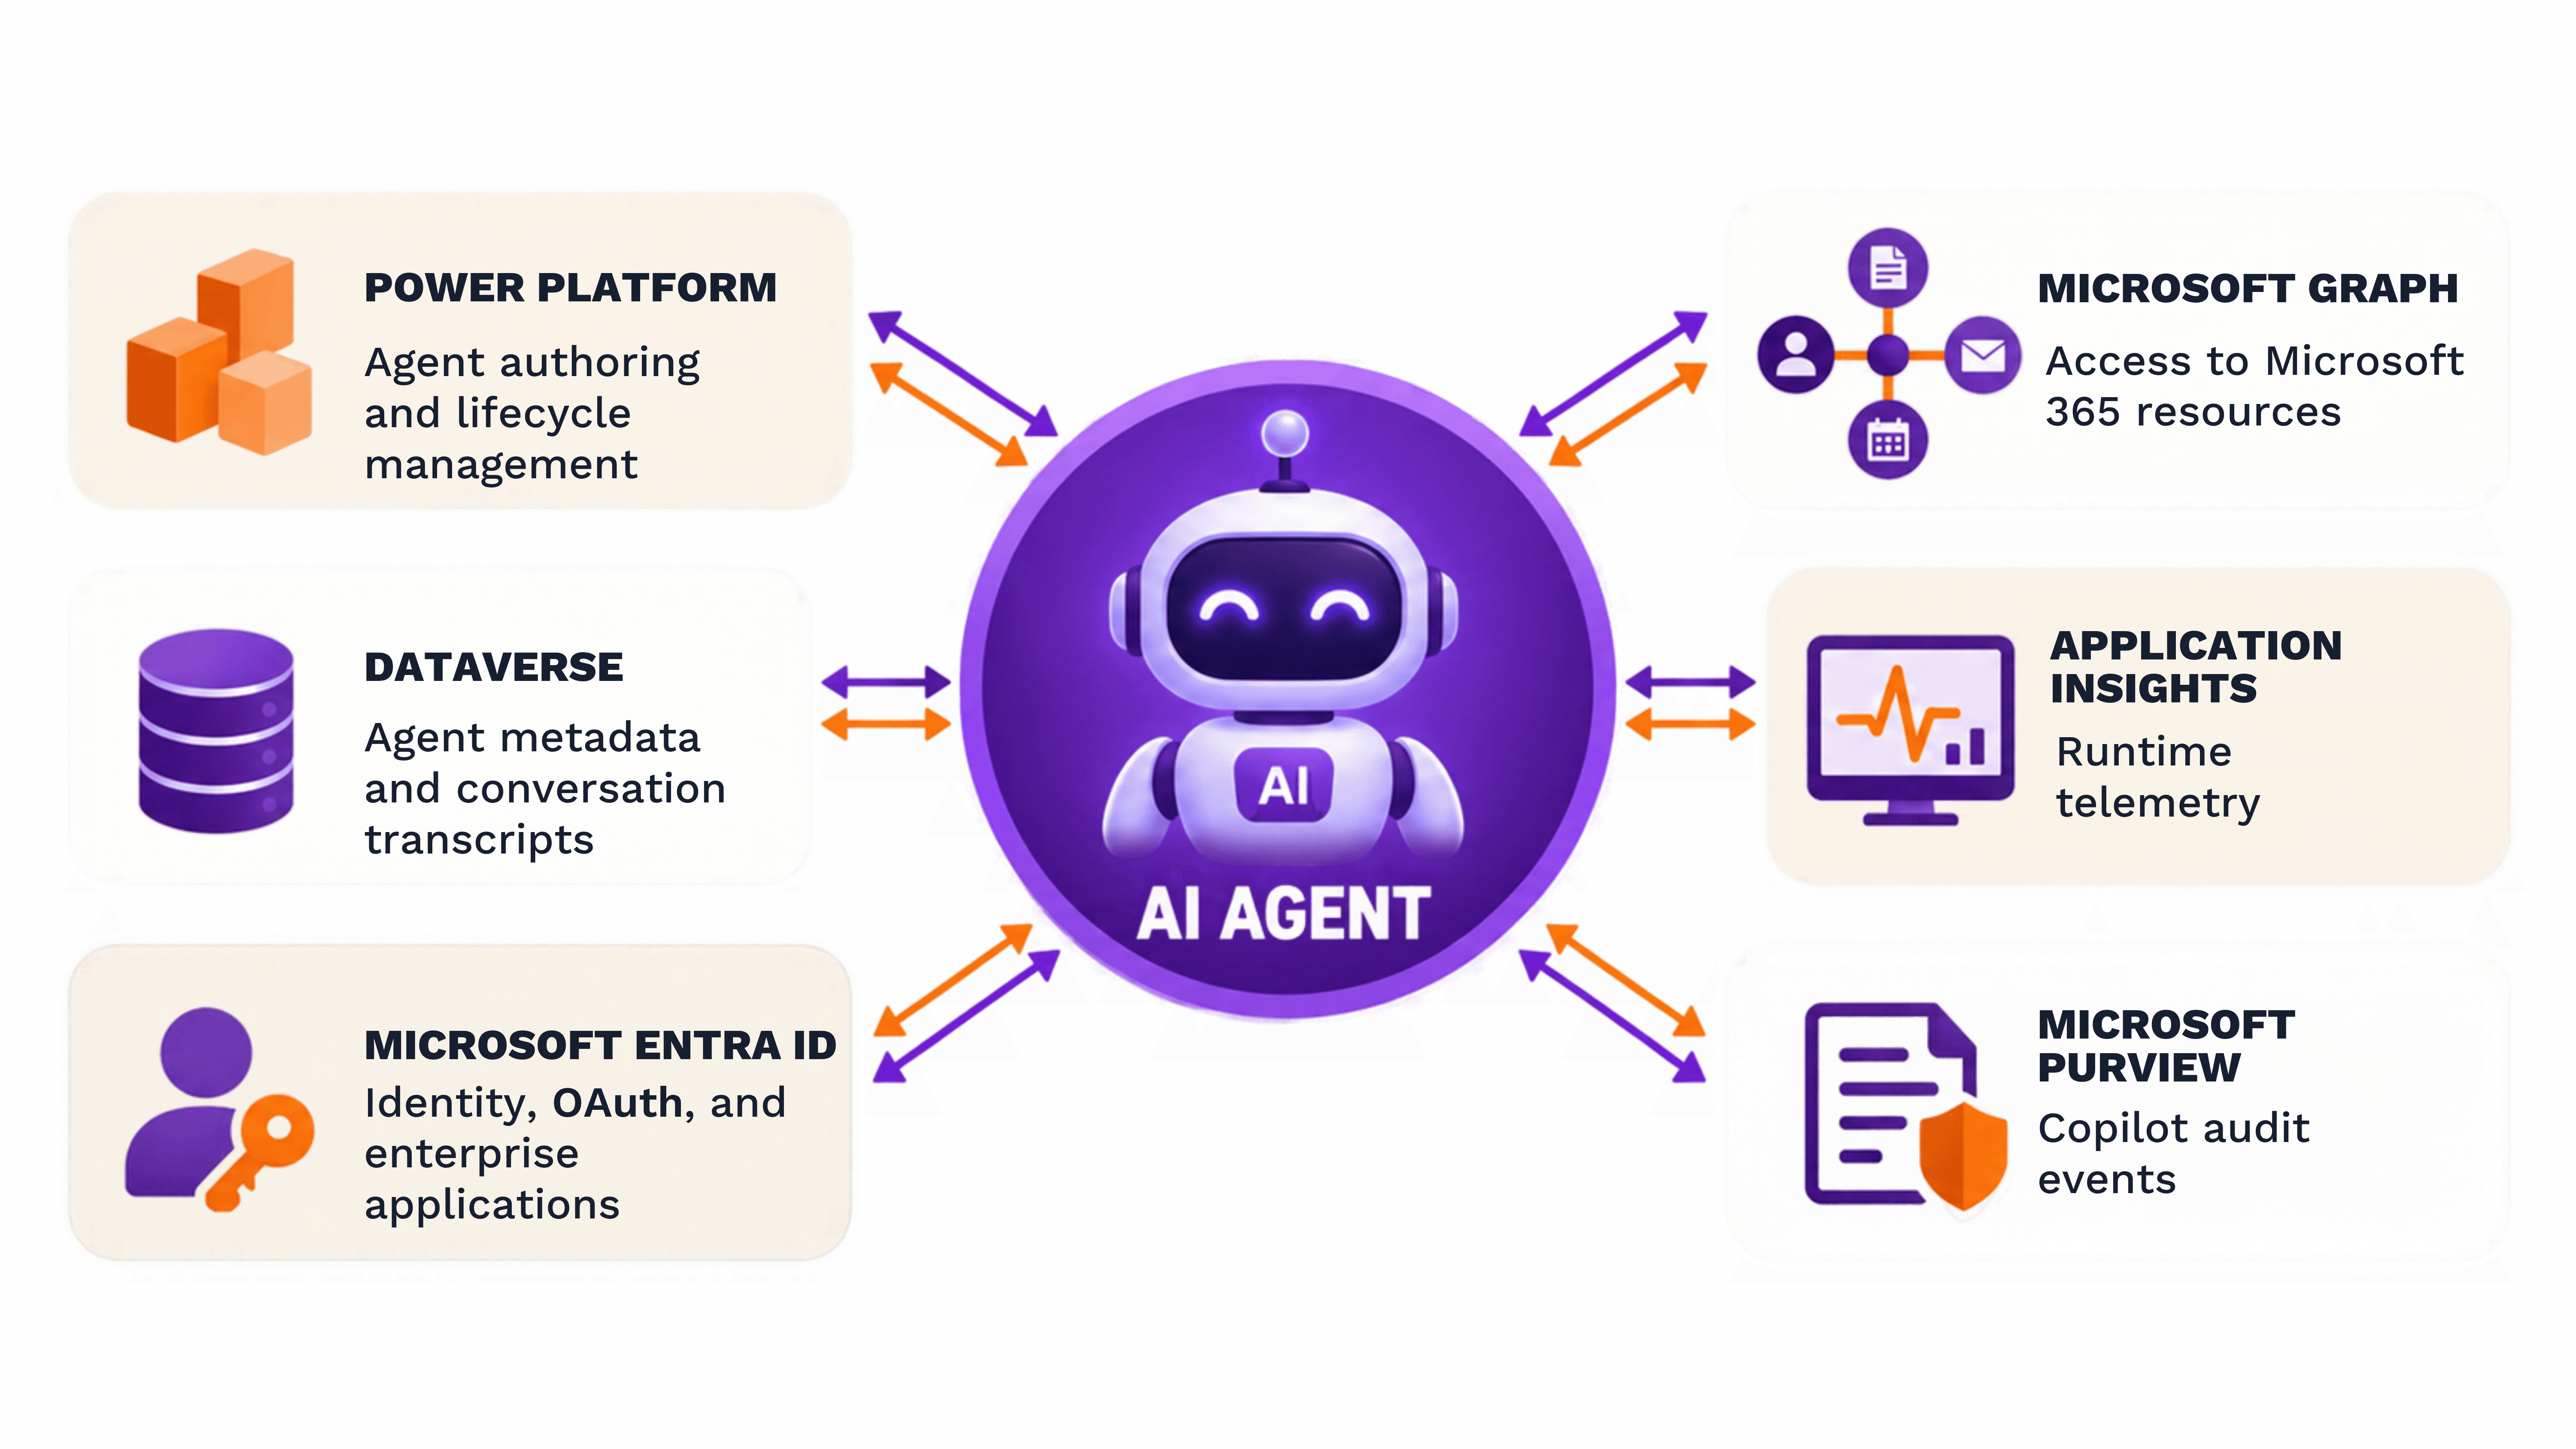
Unlike Microsoft Foundry or AWS Bedrock, Copilot Studio does not expose a native "model invocation log." Instead, the runtime is distributed across these services.
Identity Lifecycle of a Copilot Studio Agent:
One of the most interesting discoveries is that creating an agent automatically provision's identity objects in Microsoft Entra ID.
When an agent is created, Copilot Studio performs the following sequence:
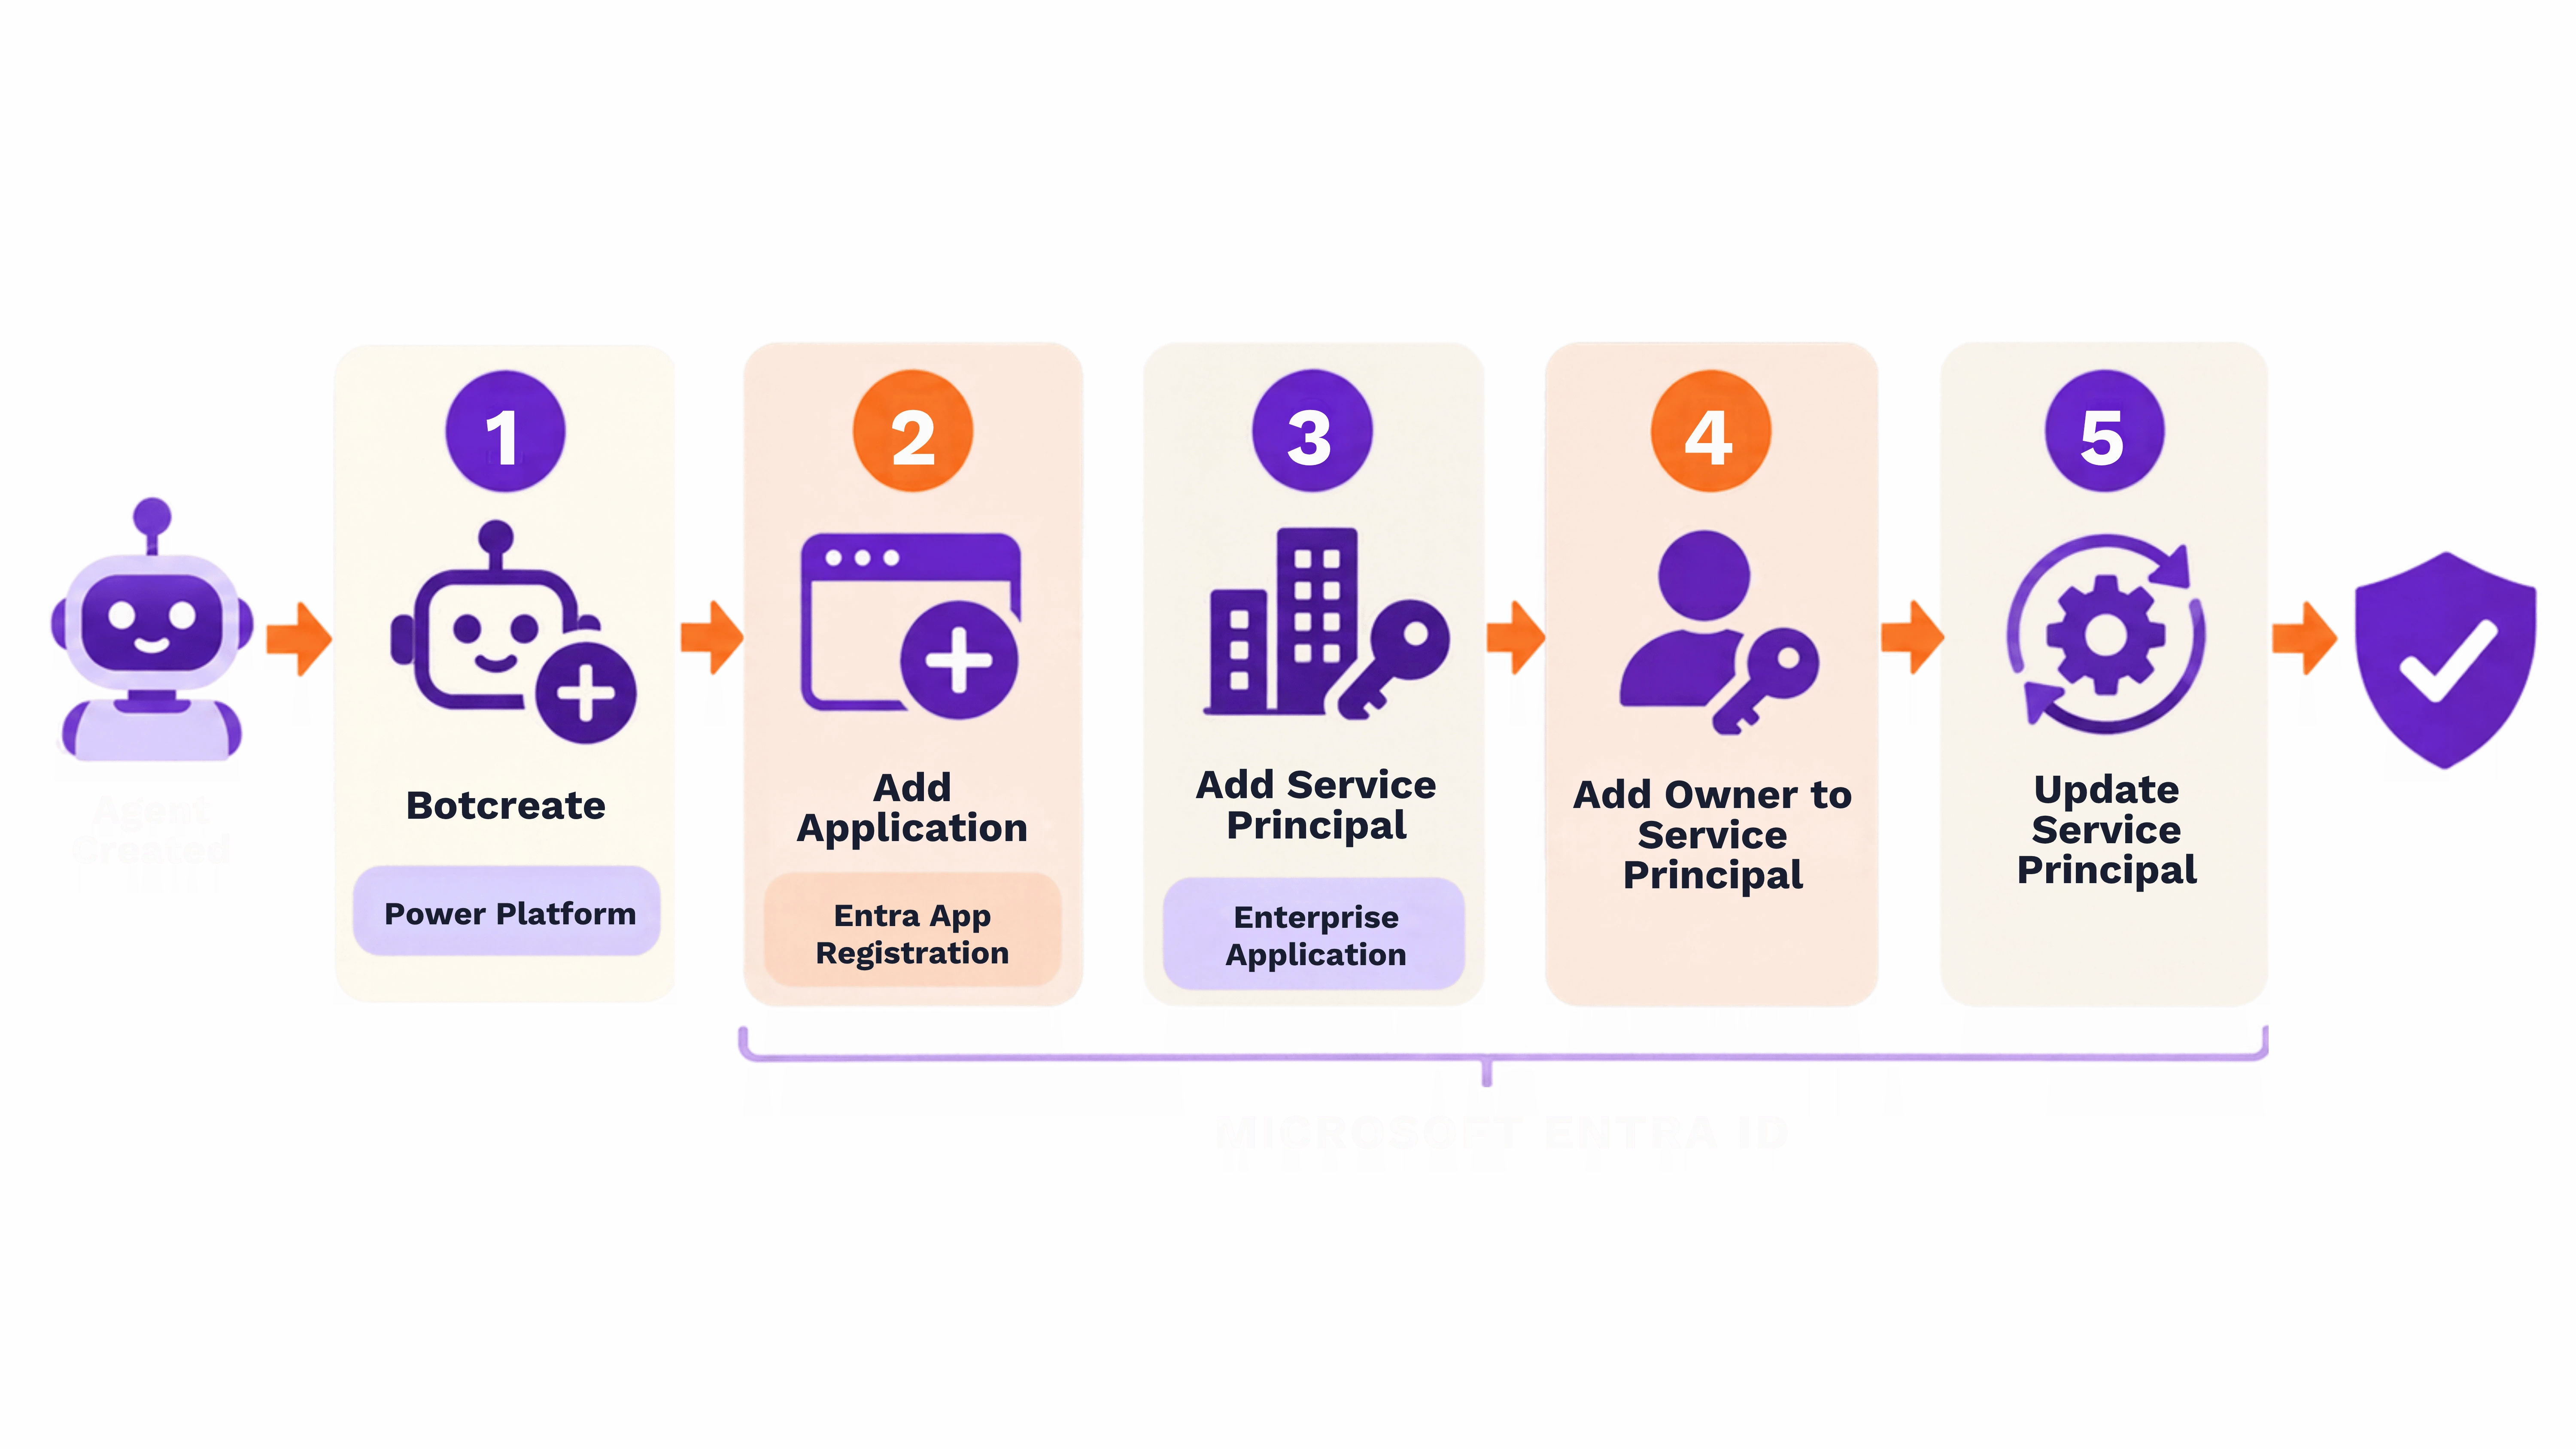
The service behind these operations is Power Virtual Agents, not the user creating the agent.
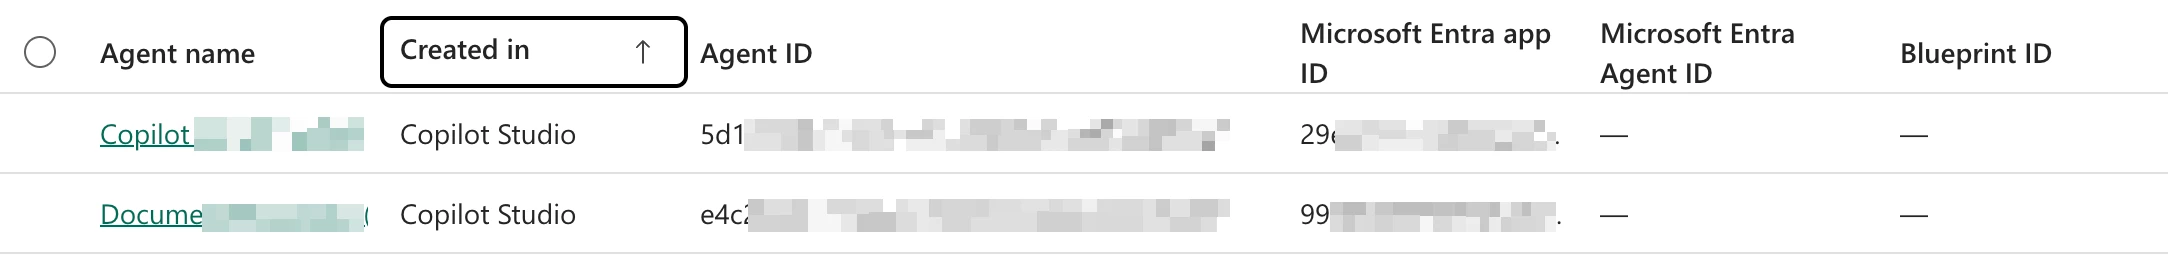
Microsoft’s newer agent identity model can represent agents through agent blueprints and agentic identities. Depending on the agent’s configuration and enabled capabilities, traditional Entra application and service principal objects may also be provisioned. Therefore, security teams should not rely solely on App Registrations to discover Copilot Studio agents
For new Copilot Studio agents after the July 2026 Agent ID rollout, you should not expect a traditional App Registration for every agent.
Microsoft says:
1. Old Copilot Studio Identity model:
Copilot Agent → App Registration / Service Principal
2. New Identity model:
Microsoft global Blueprint → Blueprint Principal in your tenant → individual Entra Agent ID
Existing agents created before the rollout continue using app registrations until they're migrated.
3. OAuth and Permission Model:
A Copilot Studio agent does not automatically receive Microsoft Graph permissions.
Access to Microsoft 365 resources is only possible after OAuth consent is granted.
A normal delegated flow looks like this:
User → Consent to application → Add delegated permission grant → Access Token → Microsoft Graph
During this process, two audit events are commonly observed.
4. Consent to application
This event records that a user (or administrator) approved an application's requested permissions.
It captures:
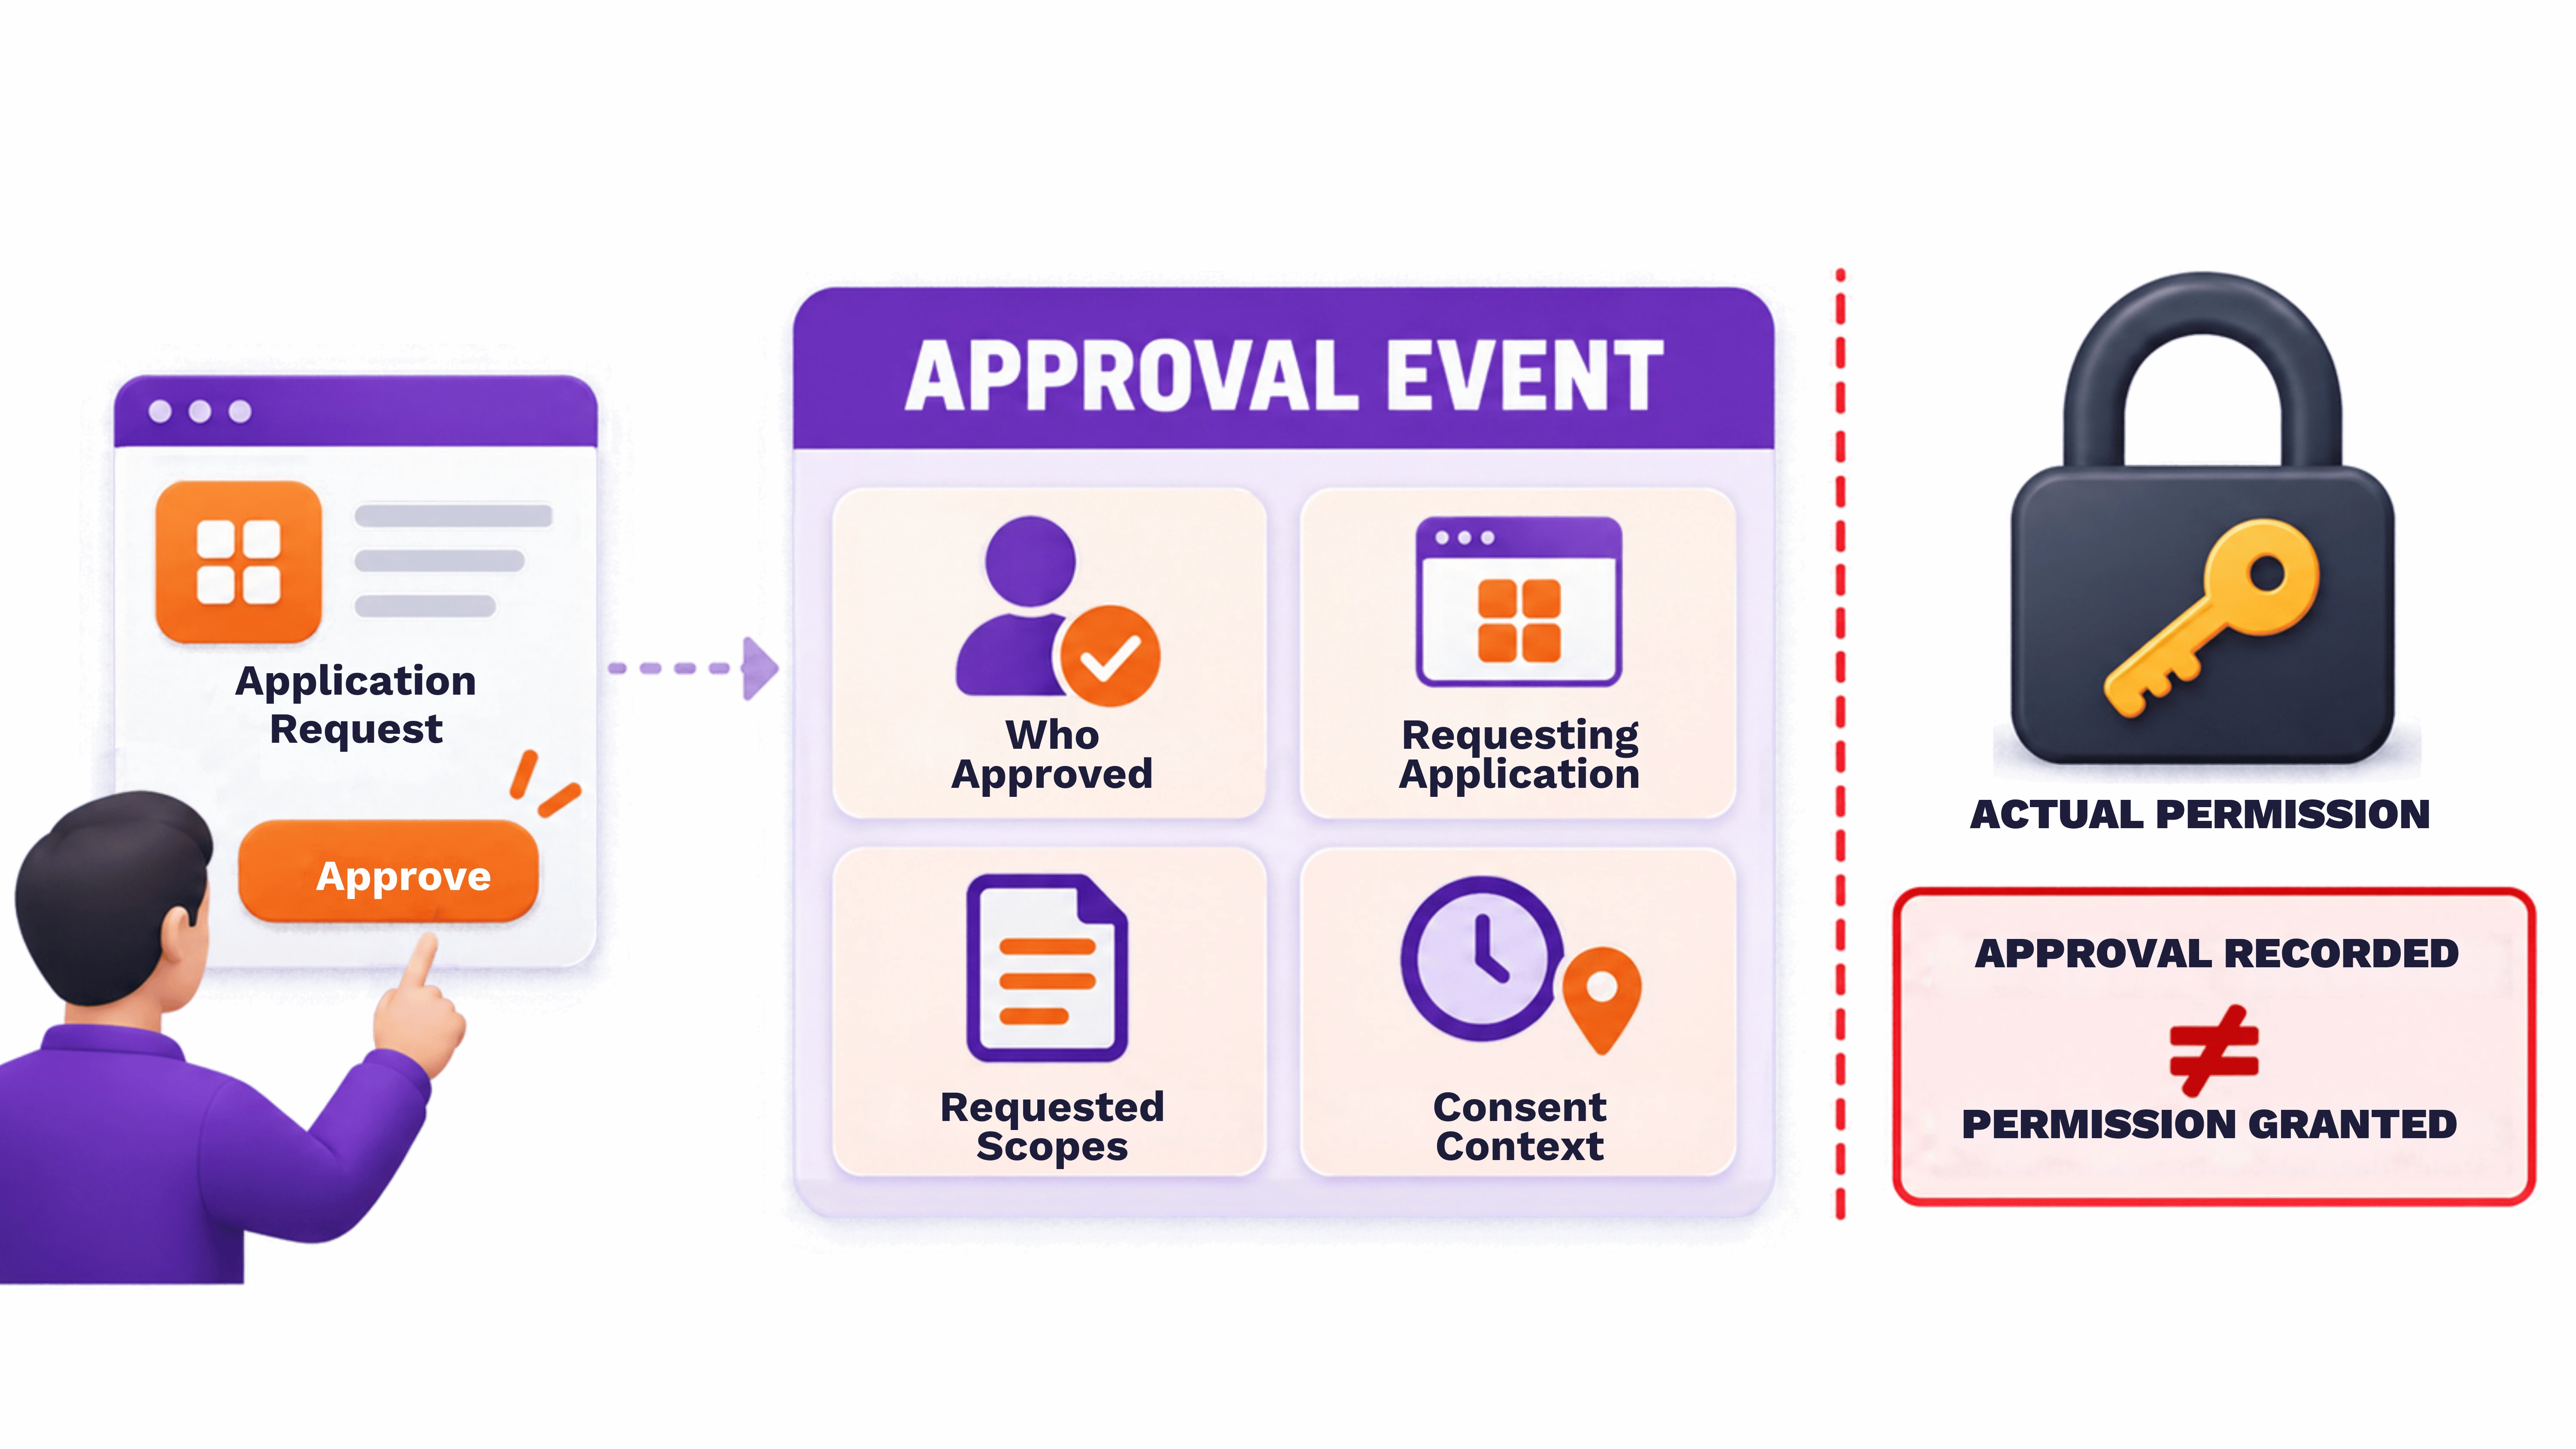
This is an approval event, not the actual permission.
5. Add delegated permission grant
This event creates the underlying OAuth2PermissionGrant object.
This event enables the application to obtain delegated access tokens.
From a security perspective, this is the most important OAuth event.
Logging Architecture
Telemetry is spread across several services.
1. Microsoft Purview
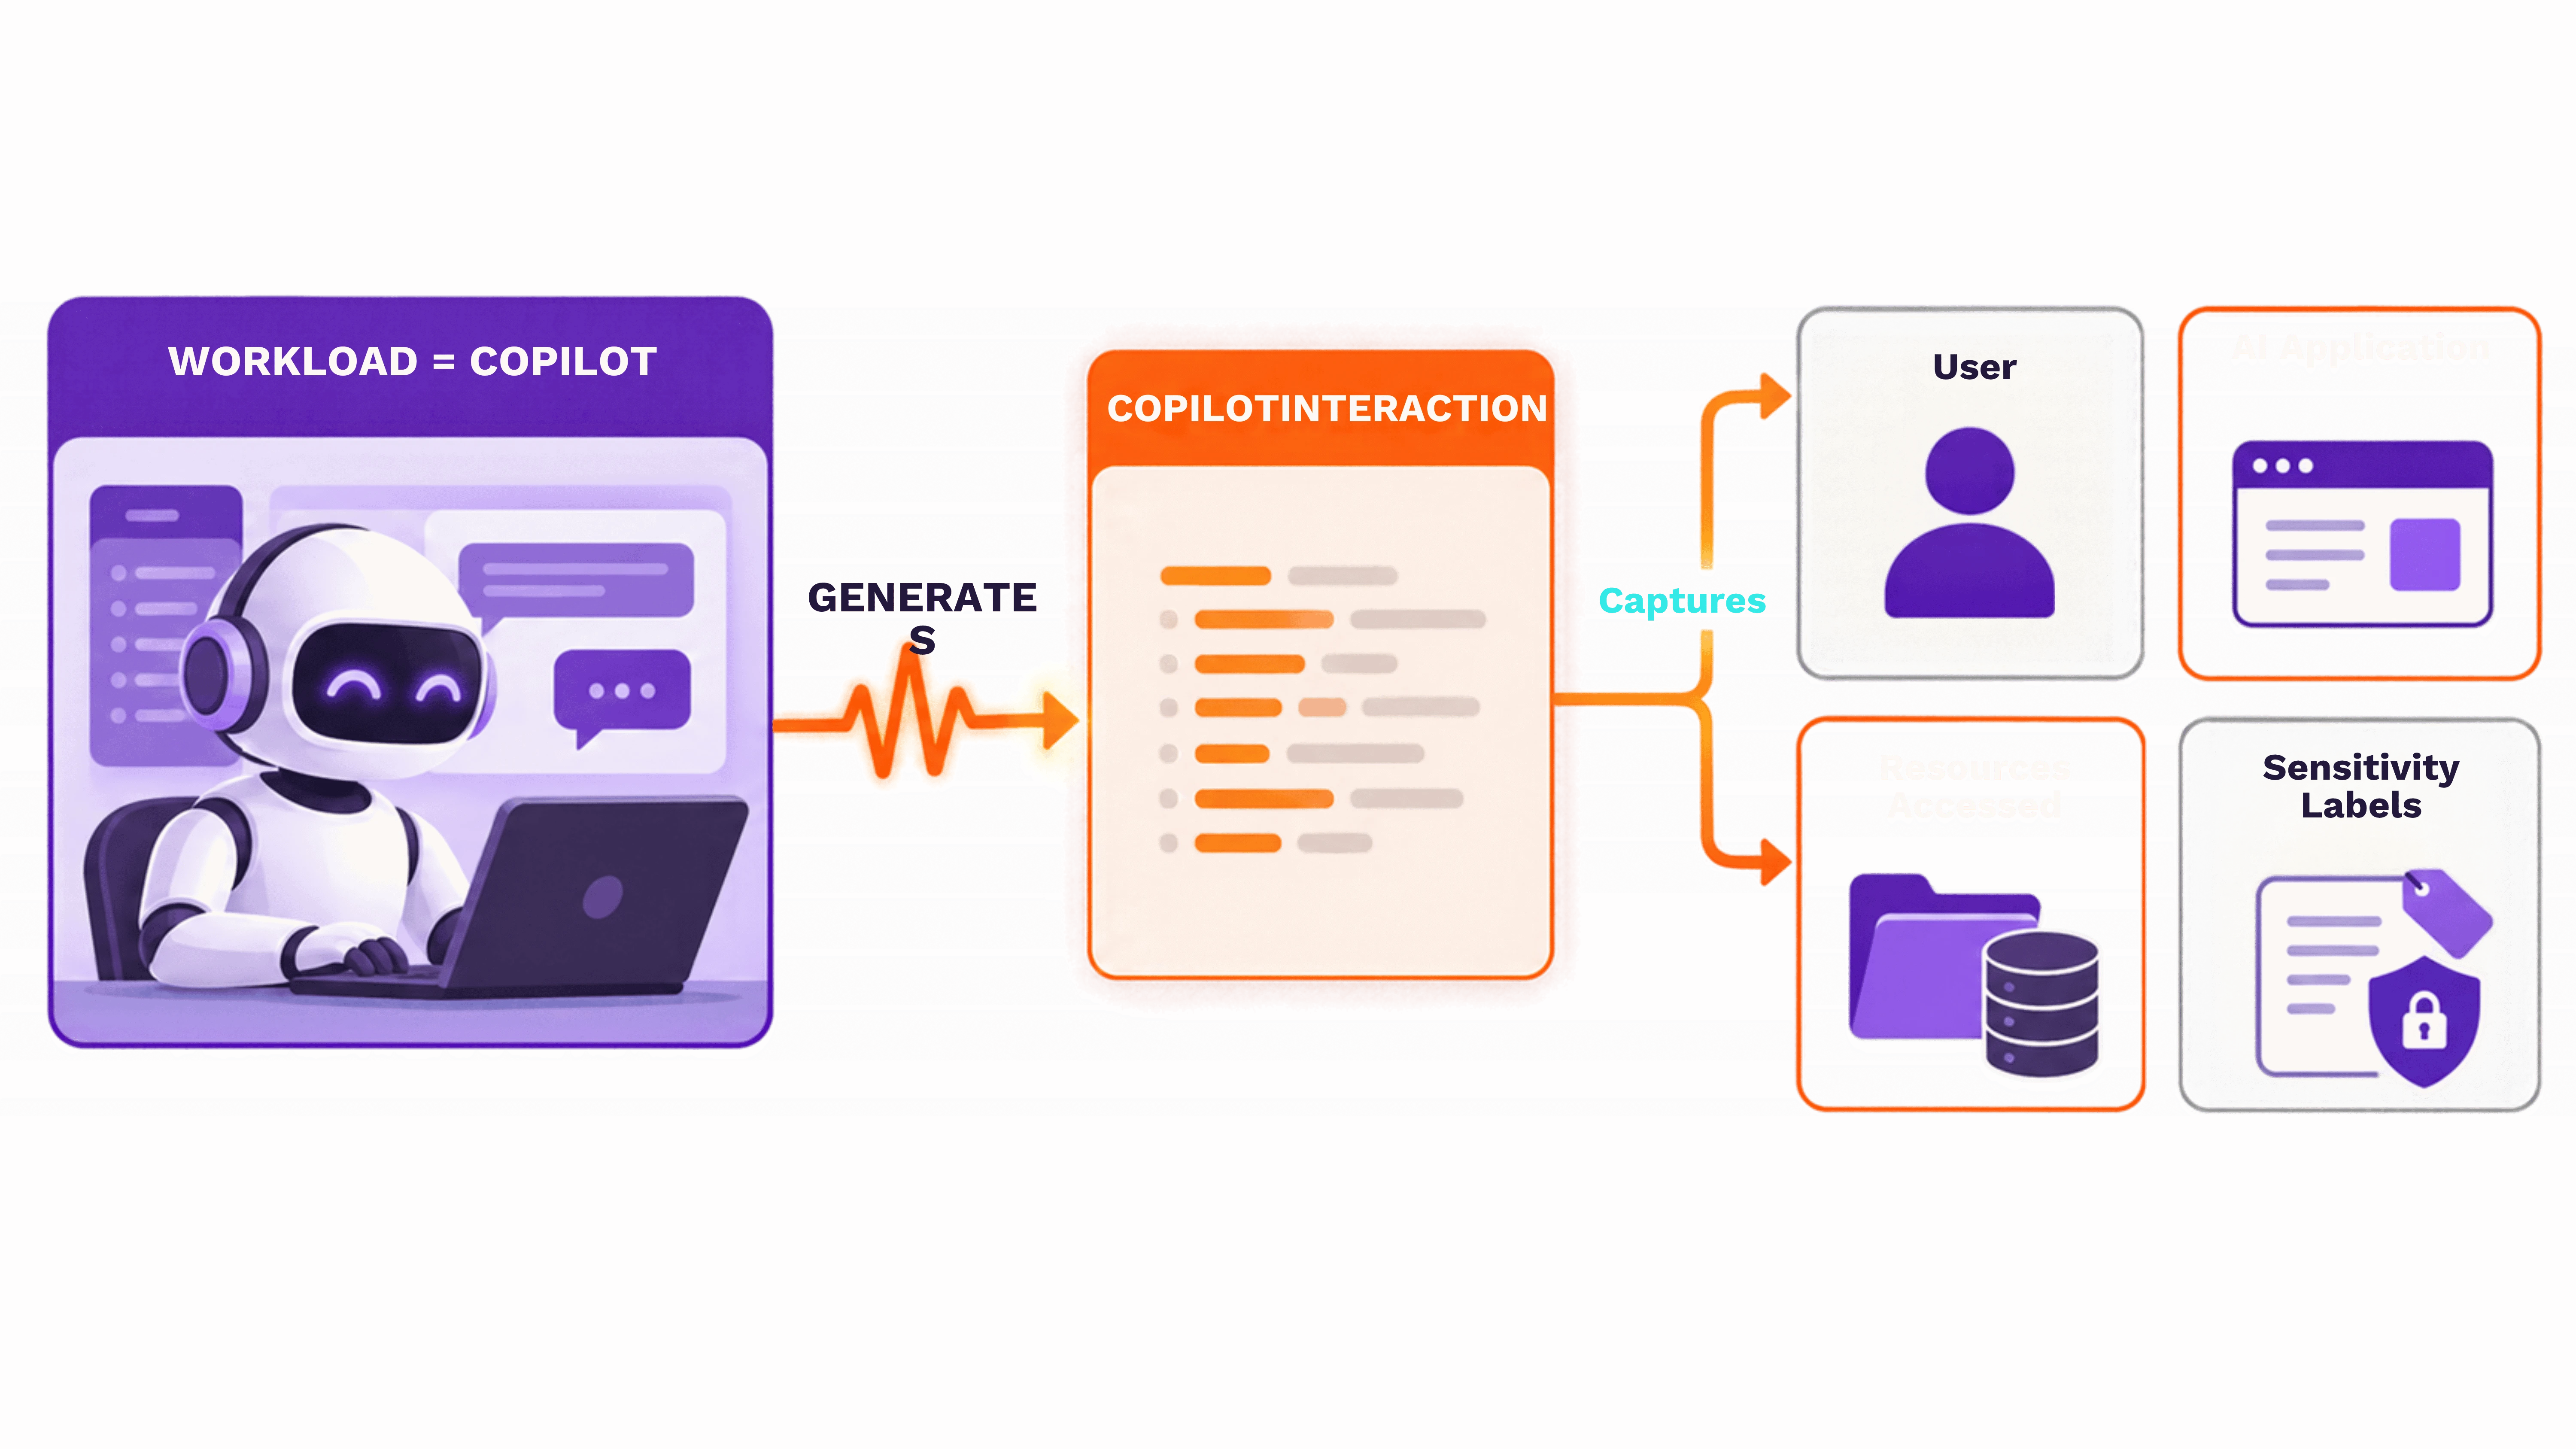
Purview does not record the actual prompt or response.
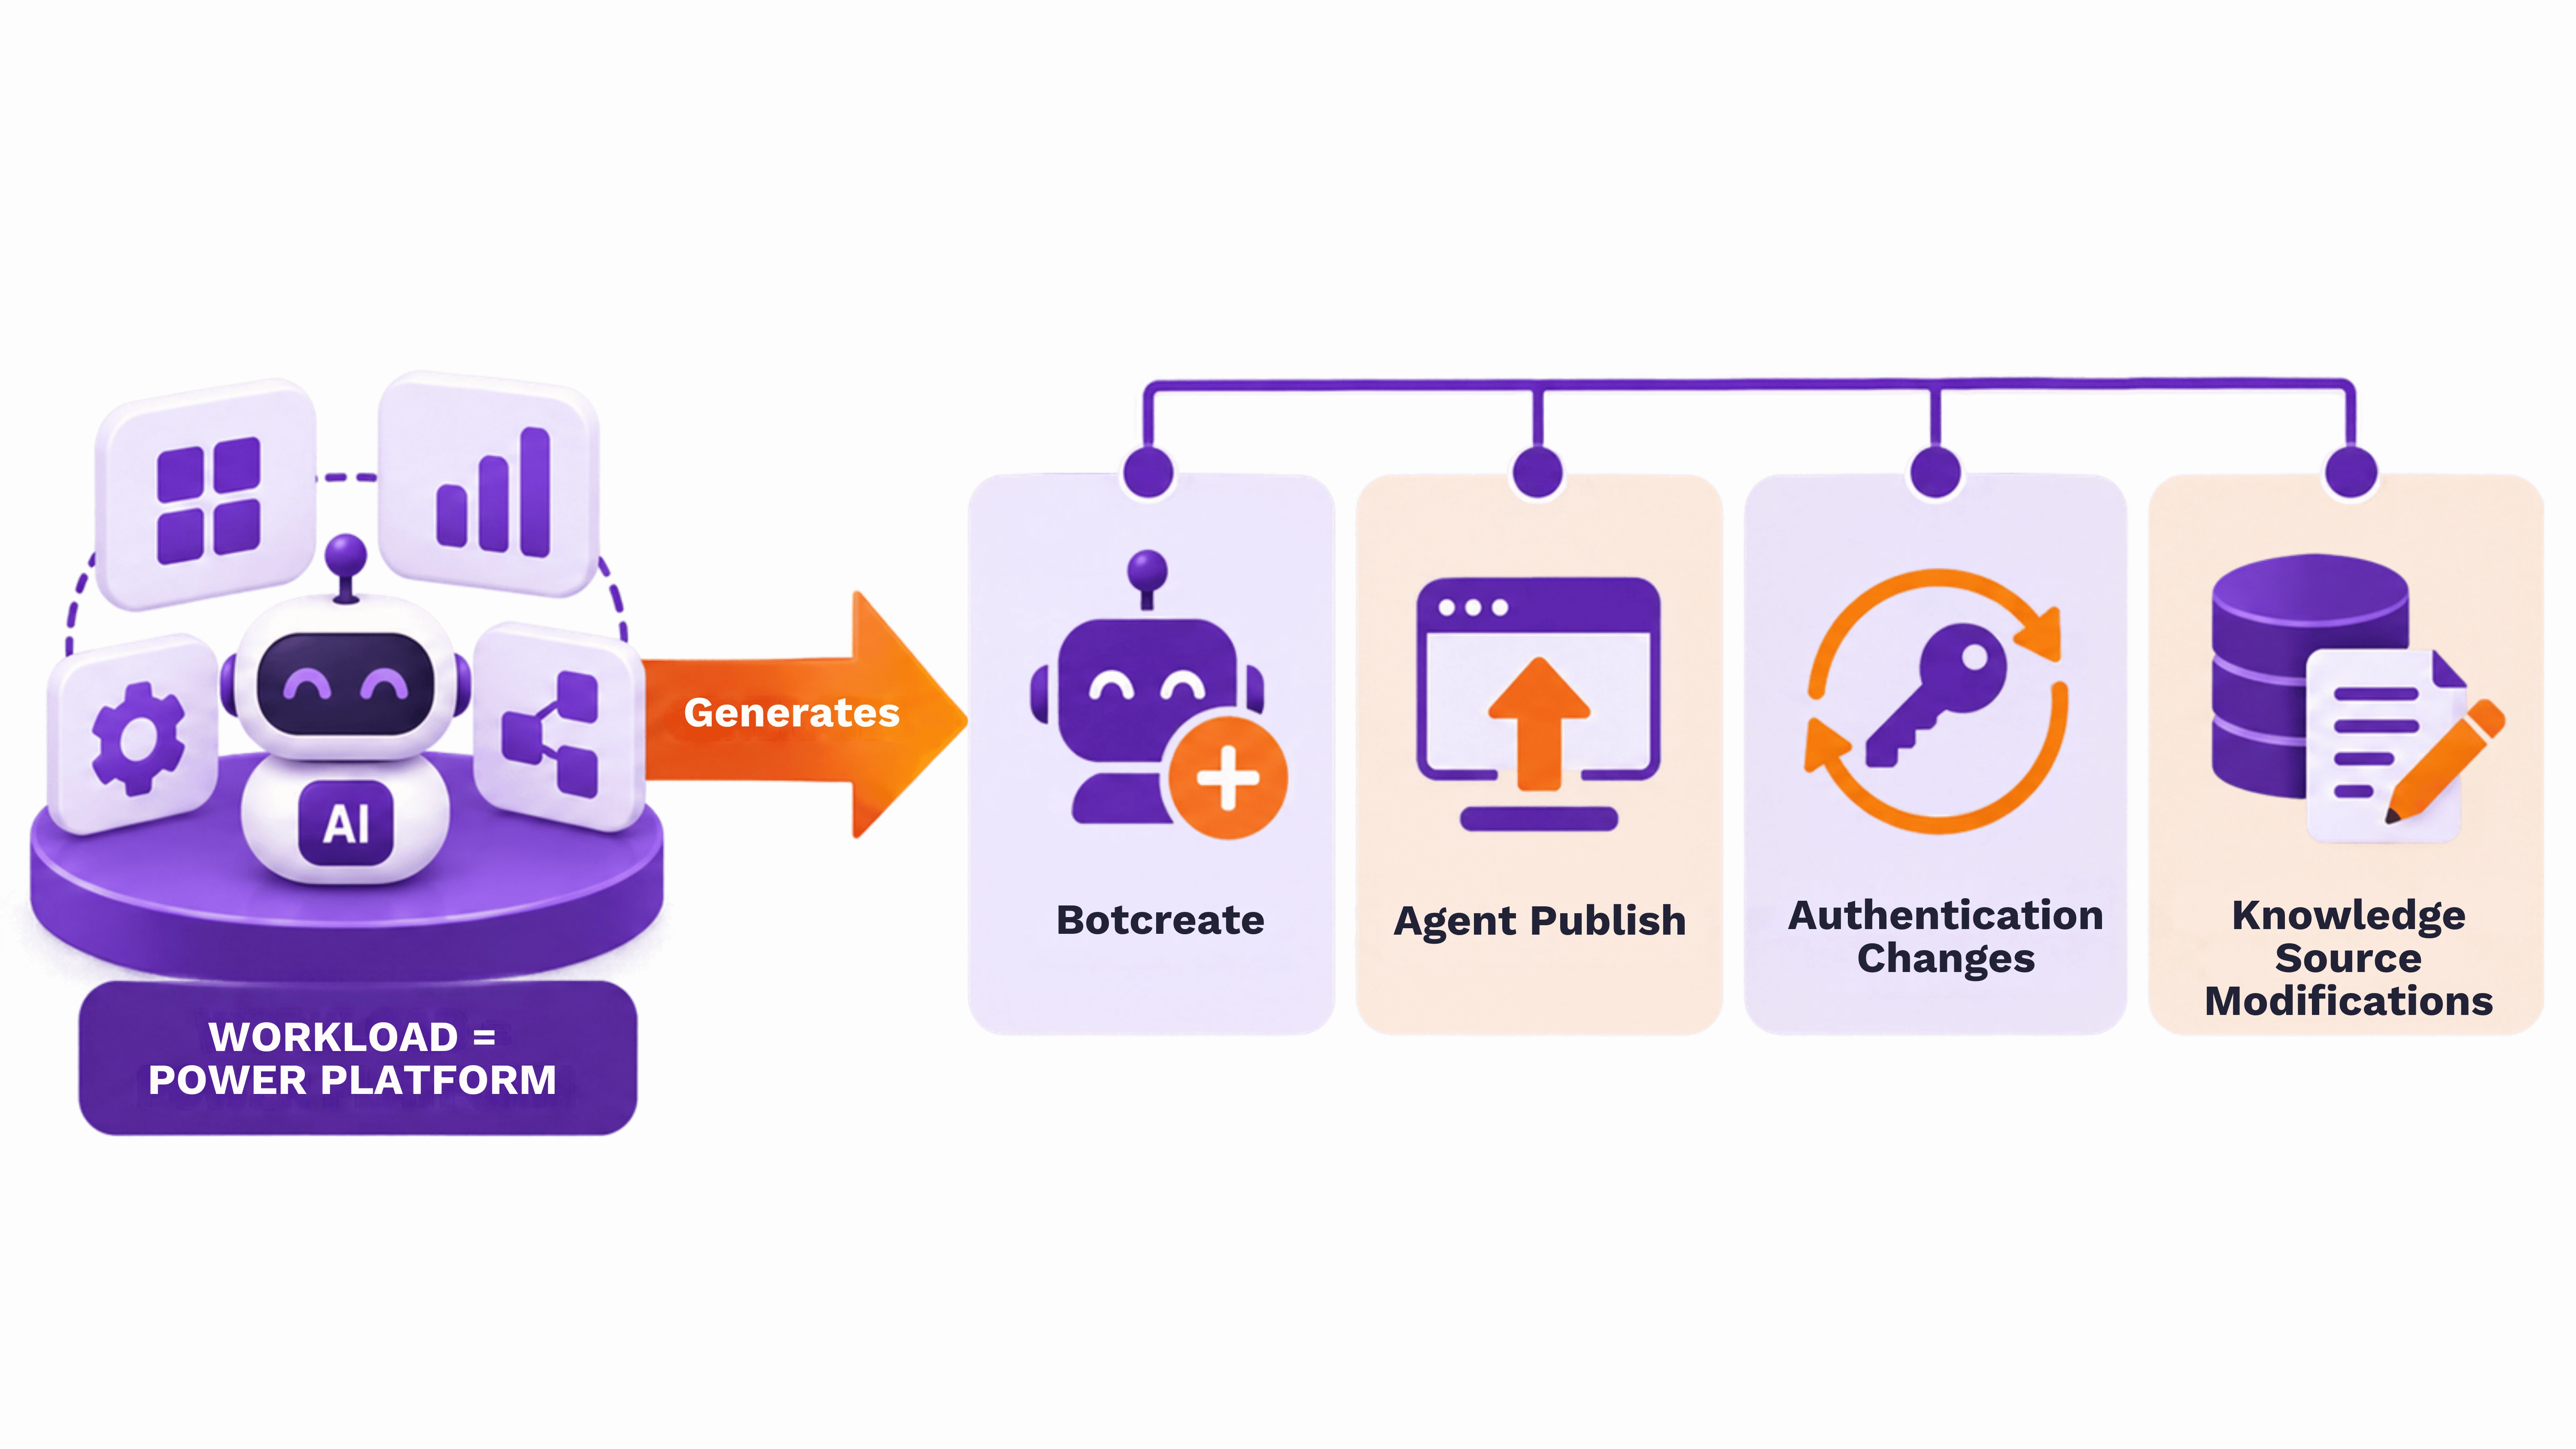
Both Copilot and Power Platform workload logs are under Audit.General content type, these logs can be fetched using the office365 connector to Securonix SIEM.
Integration Guide: https://documentation.securonix.com/r/content/active-deployment-guides/microsoft-office-o365-api.htm
2. Microsoft Entra ID
Entra remains the authoritative source for:
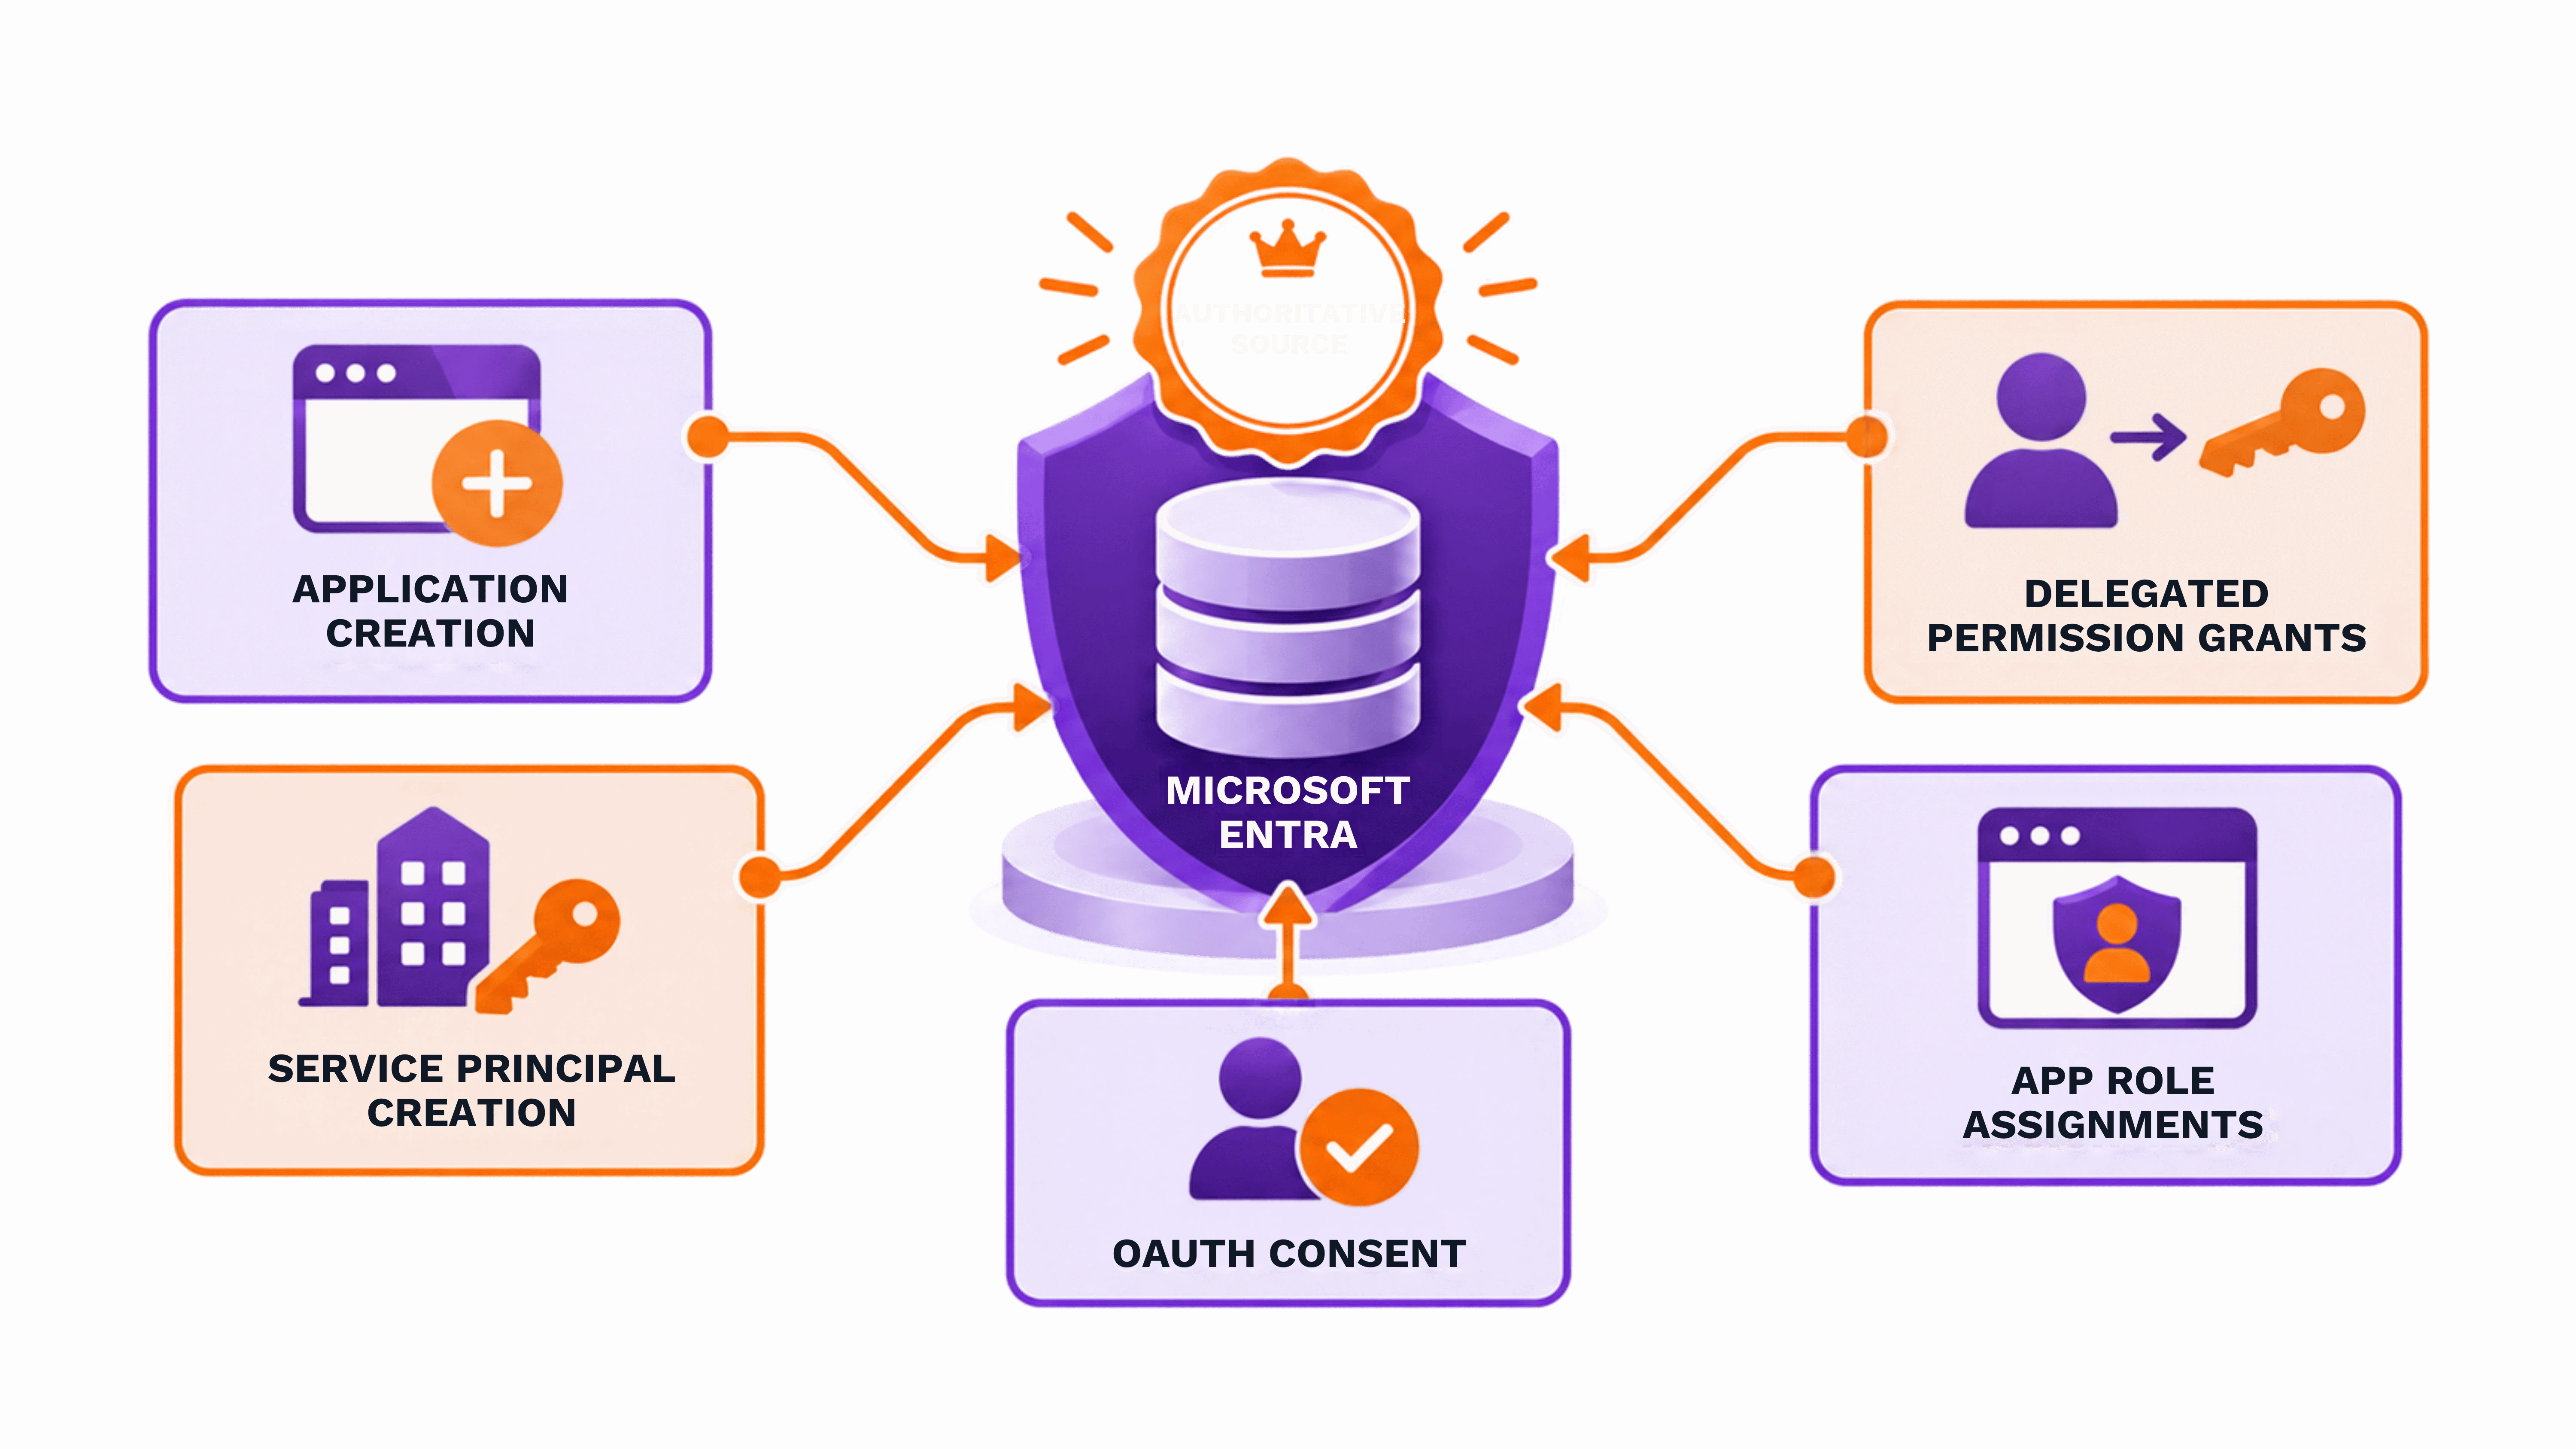
Microsoft Entra ID (Azure Active Directory) audit logs are under Audit.AzureActiveDirectory content type, these logs can also be fetched using the office365 connector to Securonix SIEM.
Integration Guide: https://documentation.securonix.com/r/content/active-deployment-guides/microsoft-office-o365-api.htm
Threat Detection Strategy:
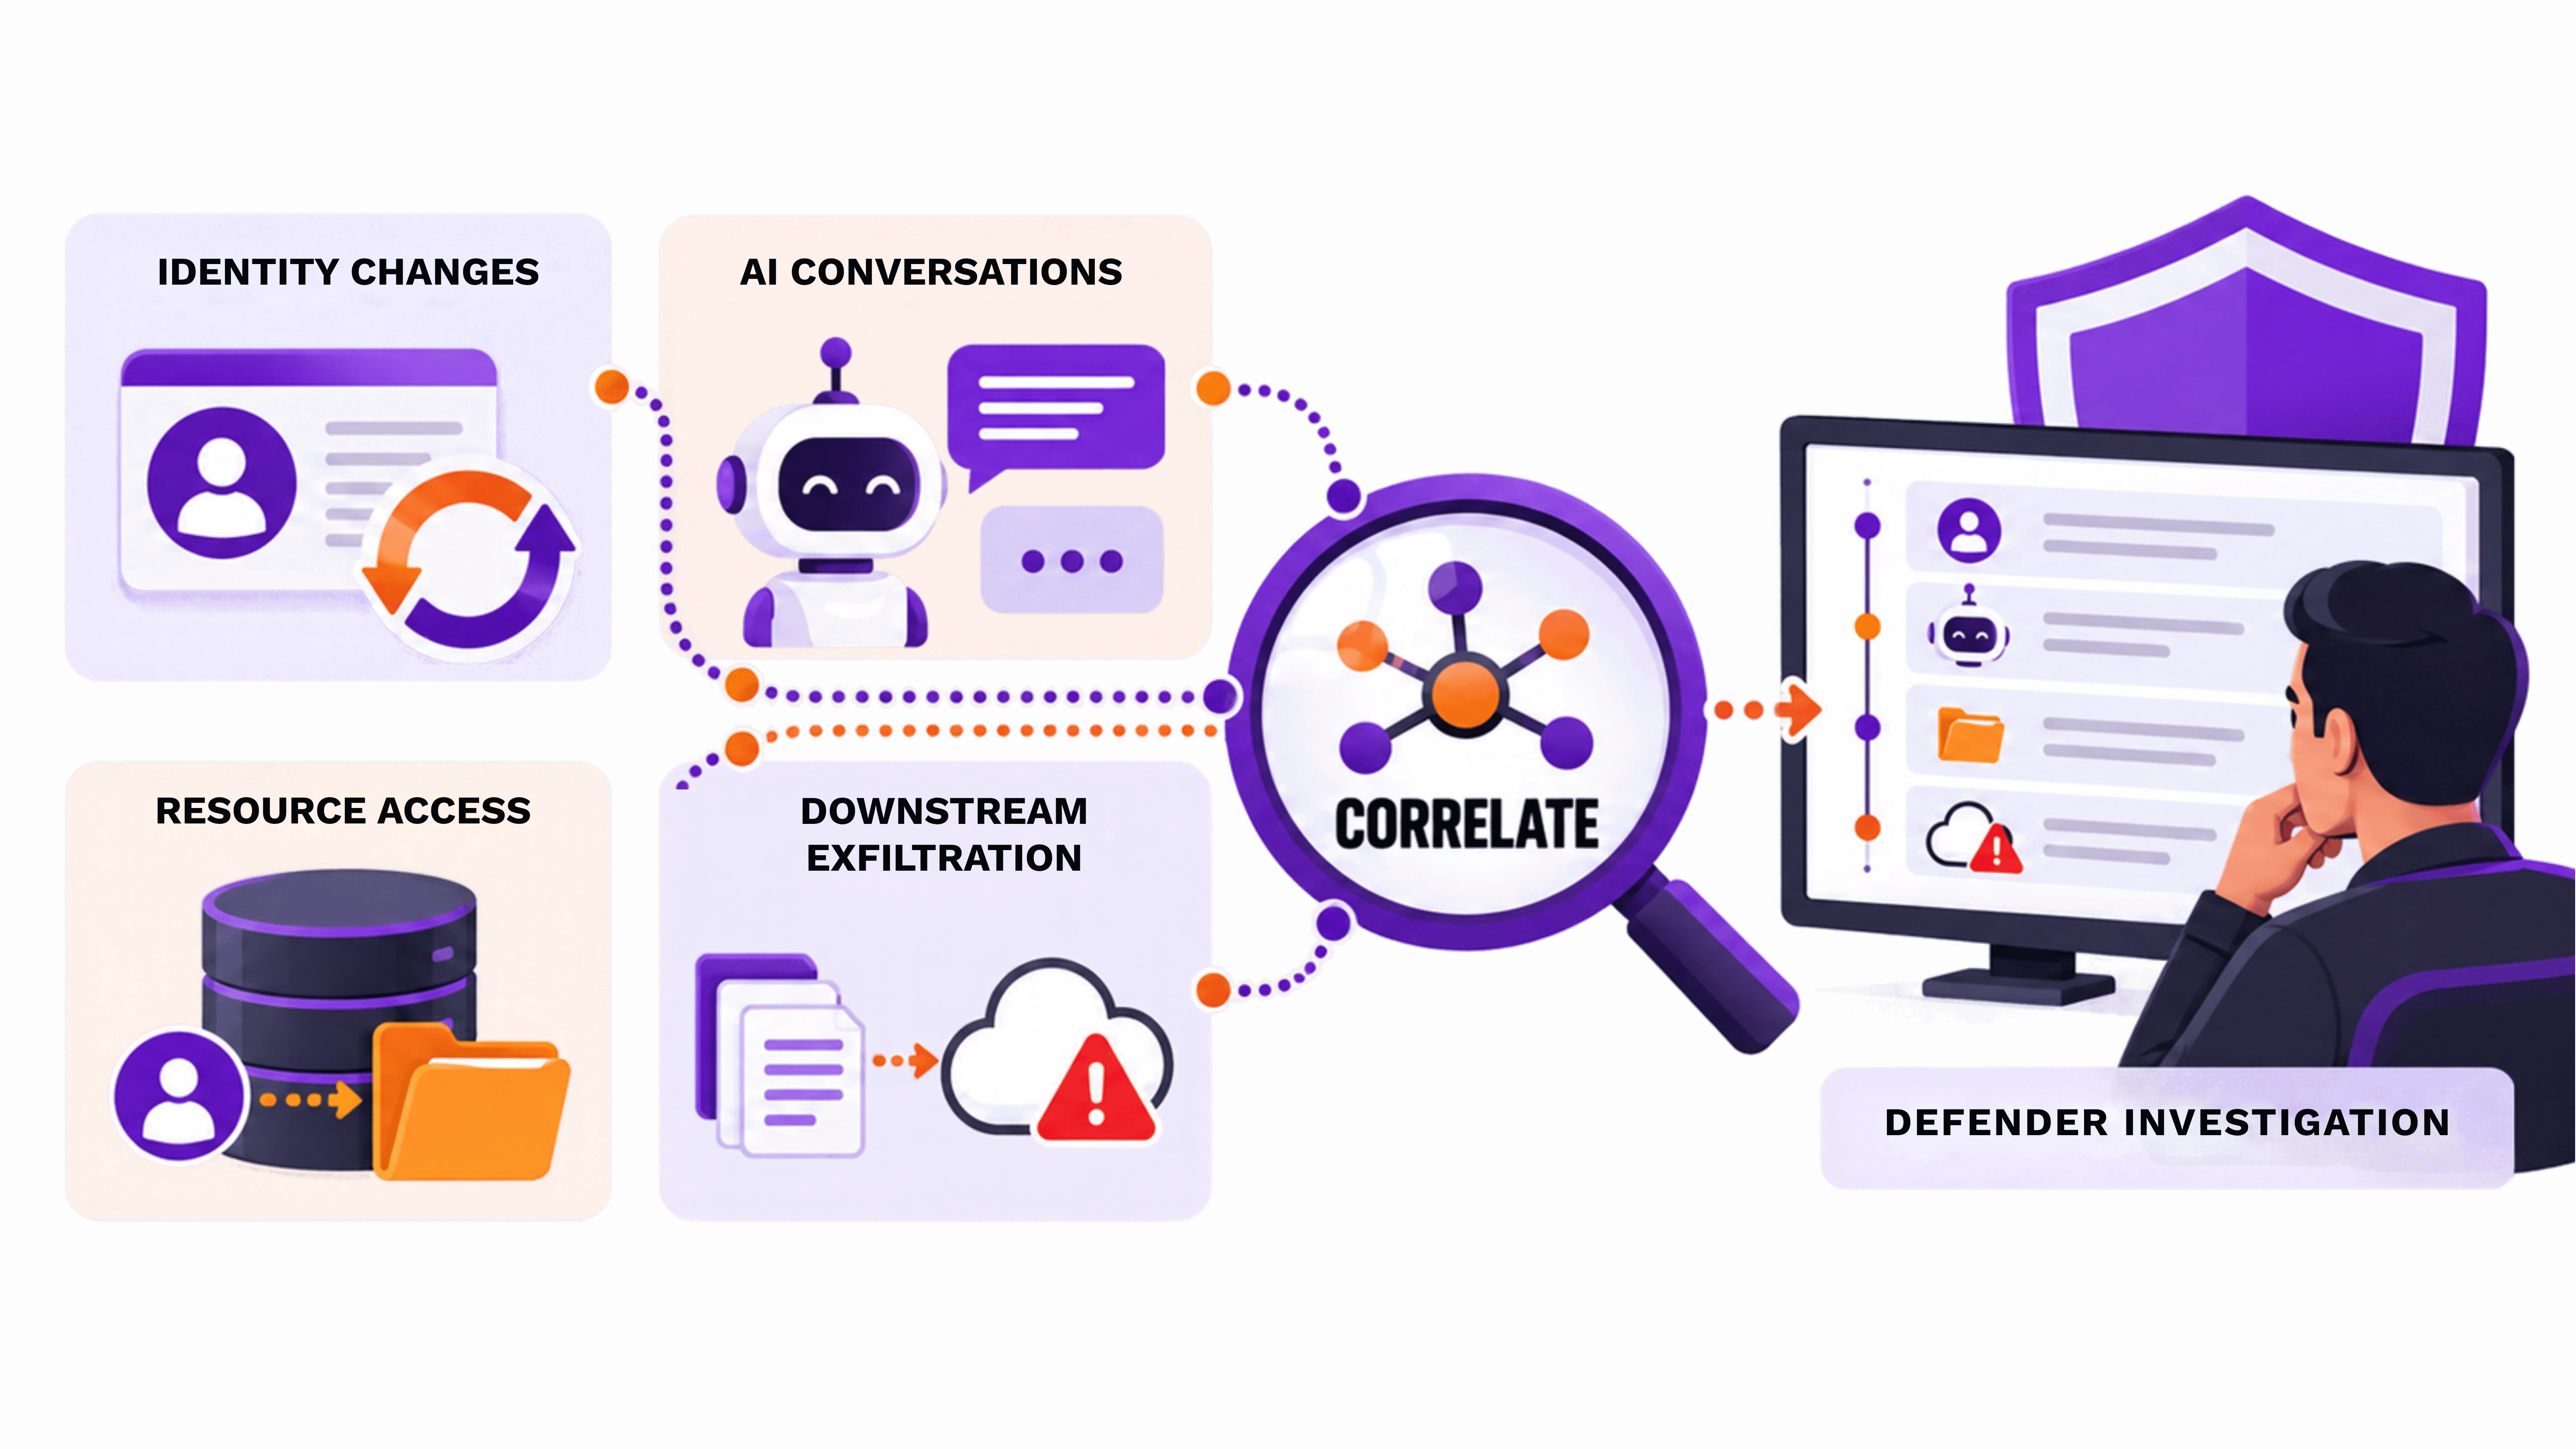
Rather than relying on a single event, detections should follow the lifecycle of the agent.
A typical attack sequence may resemble:
Agent Created → OAuth Consent → Delegated Permission Grant → Conversation/CopilotInteraction → Graph / SharePoint Access → Data Movement
This allows defenders to correlate:
Threat Detection Policies

Verification checklist
Confirm that:
- Copilot Studio administrative and interaction audit events are available for investigation.
CopilotInteractionevents can be identified in collected telemetry.- Microsoft Entra audit activity is being ingested into Securonix.
Consent to applicationevents are visible.Add delegated permission grantevents are visible.- New Entra Agent IDs can be distinguished from legacy application identities.
- Relevant downstream Microsoft 365 access telemetry is available.
- Detection policies correlate identity, permission, interaction, and resource-access activity rather than relying only on isolated events.
Call to action
After configuring the required Microsoft telemetry in Securonix, validate the event flow with a test agent and use lifecycle-based correlation to identify unusual agent creation, permission grants, interactions, and sensitive data access.