name: 'GRIMWEDGE Persistence Scheduled Task Creation Analytic'
signatureid: WEL-ACC83-RUN
category: 'Persistence'
threatname: 'Scheduled Task/Job: Scheduled Task'
functionality: 'Microsoft Windows'
lifecycle: experimental

description: |
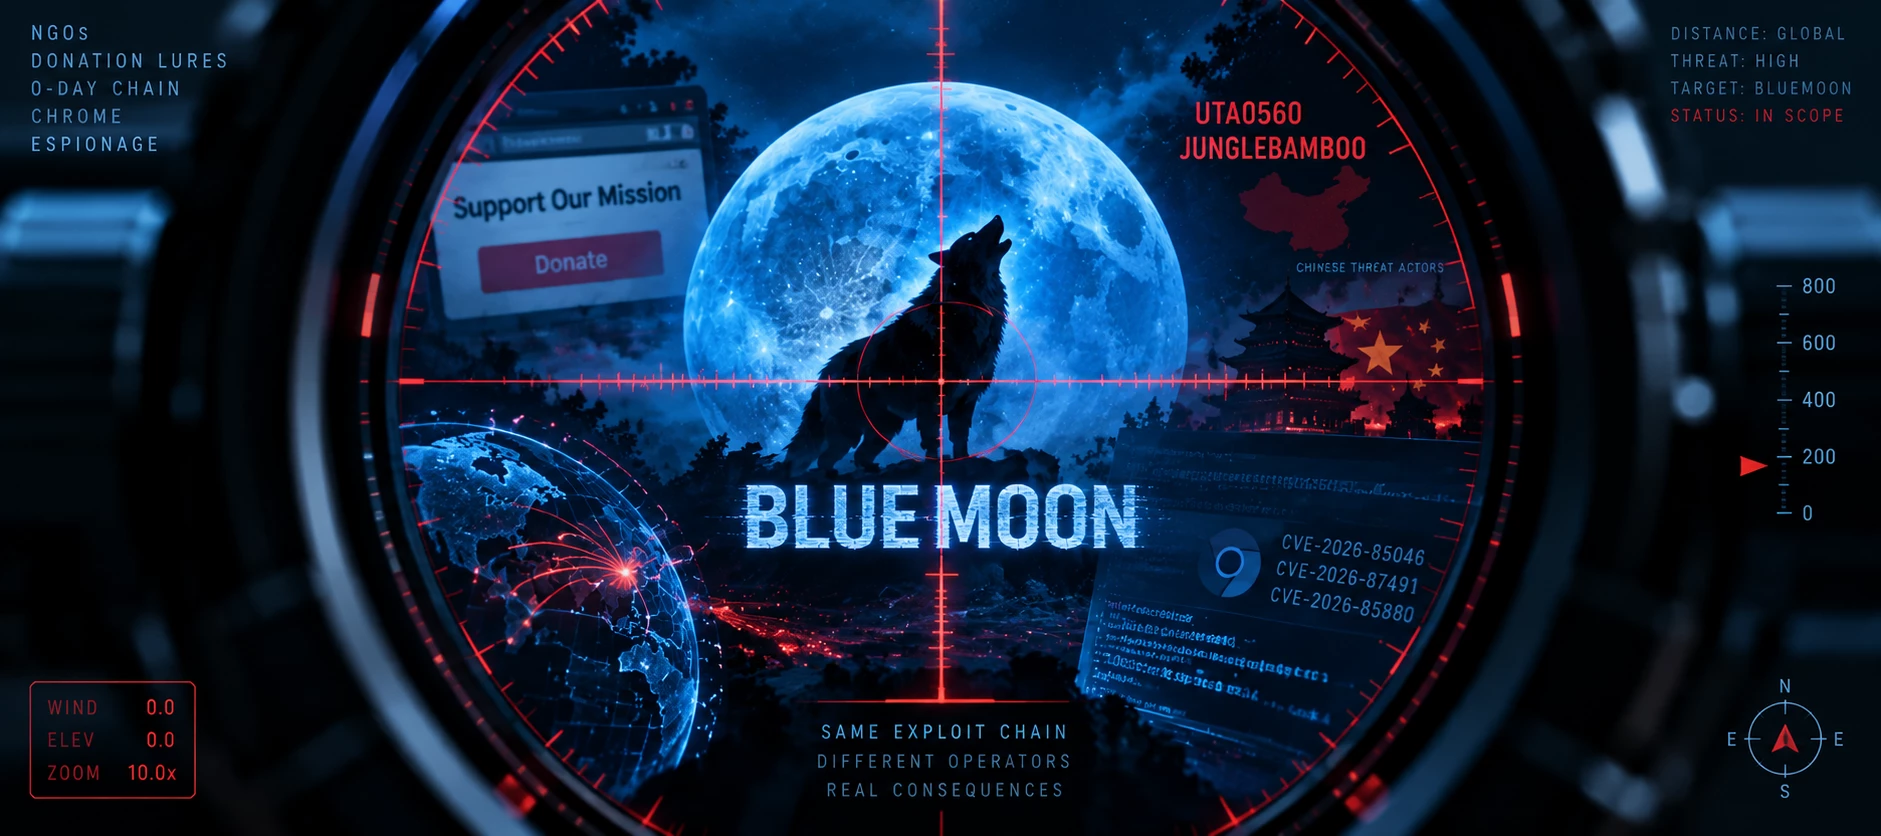
  Detects creation of a Windows scheduled task named "Windows Scheduled System" — the persistence
  mechanism used by GRIMWEDGE, the backdoor UTA0560 (a Chinese threat actor) drops after chaining
  CVE-2026-85046 (Chrome V8 type confusion), CVE-2026-87491 (V8 WebAssembly sandbox escape), and
  CVE-2026-85880 (Windows ALPC/RtlpCreateServerAcl privilege escalation) via the BlueMoon exploit
  kit. The task re-runs wsc.dll's DLL side-loading chain every five minutes, giving GRIMWEDGE (a
  compact in-memory backdoor running inside msiexec.exe) durable re-execution even if the initial
  process is killed. Per Volexity, UTA0560 recompiled the dropper and loader on September 2, 2026 —
  one day after first use — while keeping this task name, its 5-minute cadence, and the C2 URL
  pattern unchanged, making the task name a more durable detection surface than any single file hash.
reference:
  - https://www.volexity.com/blog/2026/09/09/mind-the-patch-gap-multiple-chinese-threat-actors-chain-0-day-exploits-in-chrome-windows/
  - https://www.proofpoint.com/us/blog/threat-insight/once-bluemoon-multiple-state-aligned-threat-actors-rapidly-adopt-novel-exploit
  - https://www.bleepingcomputer.com/news/security/new-bluemoon-kit-exploited-windows-and-chrome-zero-day-flaws/
  - https://www.cisa.gov/news-events/alerts/2026/09/04/cisa-adds-one-known-exploited-vulnerability-catalog
labels:
  - attack.persistence
  - attack.t1053.005
  - attack.t1203
  - attack.t1068
  - BlueMoon
  - UTA0560
  - JungleBamboo
  - GRIMWEDGE
  - CVE-2026-85046
  - CVE-2026-87491
  - CVE-2026-85880
  - China
logsource:
  product: Windows
  service: Security
detection:
  selection_task_created:
    BaseEventId: 4698    # "A scheduled task was created" (Windows Security log)
    TaskName|contains: 'Windows Scheduled System'
  selection_task_content:
    BaseEventId: 4698
    ScheduleTaskCommandLine|contains:
      - 'wsc.dll'
      - 'msiexec'
  condition: selection_task_created or selection_task_content
criticality: Critical
saveasthreat: false

verbose_info: 'A scheduled task consistent with GRIMWEDGE/BlueMoon persistence (${transactionstring1!"Windows Scheduled System"}) was created on ${devicehostname!"UNKNOWN"}'
violation_summary:
  grouping_attribute: 'DeviceHostName'
  level2_attribute: 'AccountName'
  level2_metadata_attributes:
    - TaskName
    - ScheduleTaskCommandLine
  metadata_attributes:
TECHNICAL DETAILS
Why Event ID 4698 + TaskName, not a file hash:
Volexity confirmed UTA0560 recompiled msgbox.exe and wsc.dll on September 2, 2026 (one day
into the campaign) while leaving the scheduled task's name, its 5-minute re-execution cadence,
and the GRIMWEDGE C2 URL pattern unchanged. Hash-based detection on this campaign therefore has
a short shelf life; the task name and its creation event are the durable pivot.
Scope limitation: this rule only fires on hosts where BaseEventId 4698 (Security log, "Audit
Other Object Access Events" / "Audit Non Sensitive Privilege Use" scheduled-task auditing
subcategory) is enabled and forwarded. Confirm this audit subcategory is enabled fleet-wide via
GPO before relying on this as primary coverage — it is not enabled by default on all Windows
builds.
Policy building walkthrough can be found in this previous post: