name: Gryxa Toolkit Working Directory or Component Script Referenced in Process Execution Analytic
signatureid: EDR-SYM964-RUN
category: 'Defense Evasion'
threatname: 'Masquerading: Match Legitimate Resource Name or Location'
functionality: 'Endpoint Management Systems'

description: |
  Detects process execution that references any of the four hidden working directories used by the
  Gryxa toolkit, or its named persistence/monitoring component scripts (own_lib.ps1, own_mon.cmd).
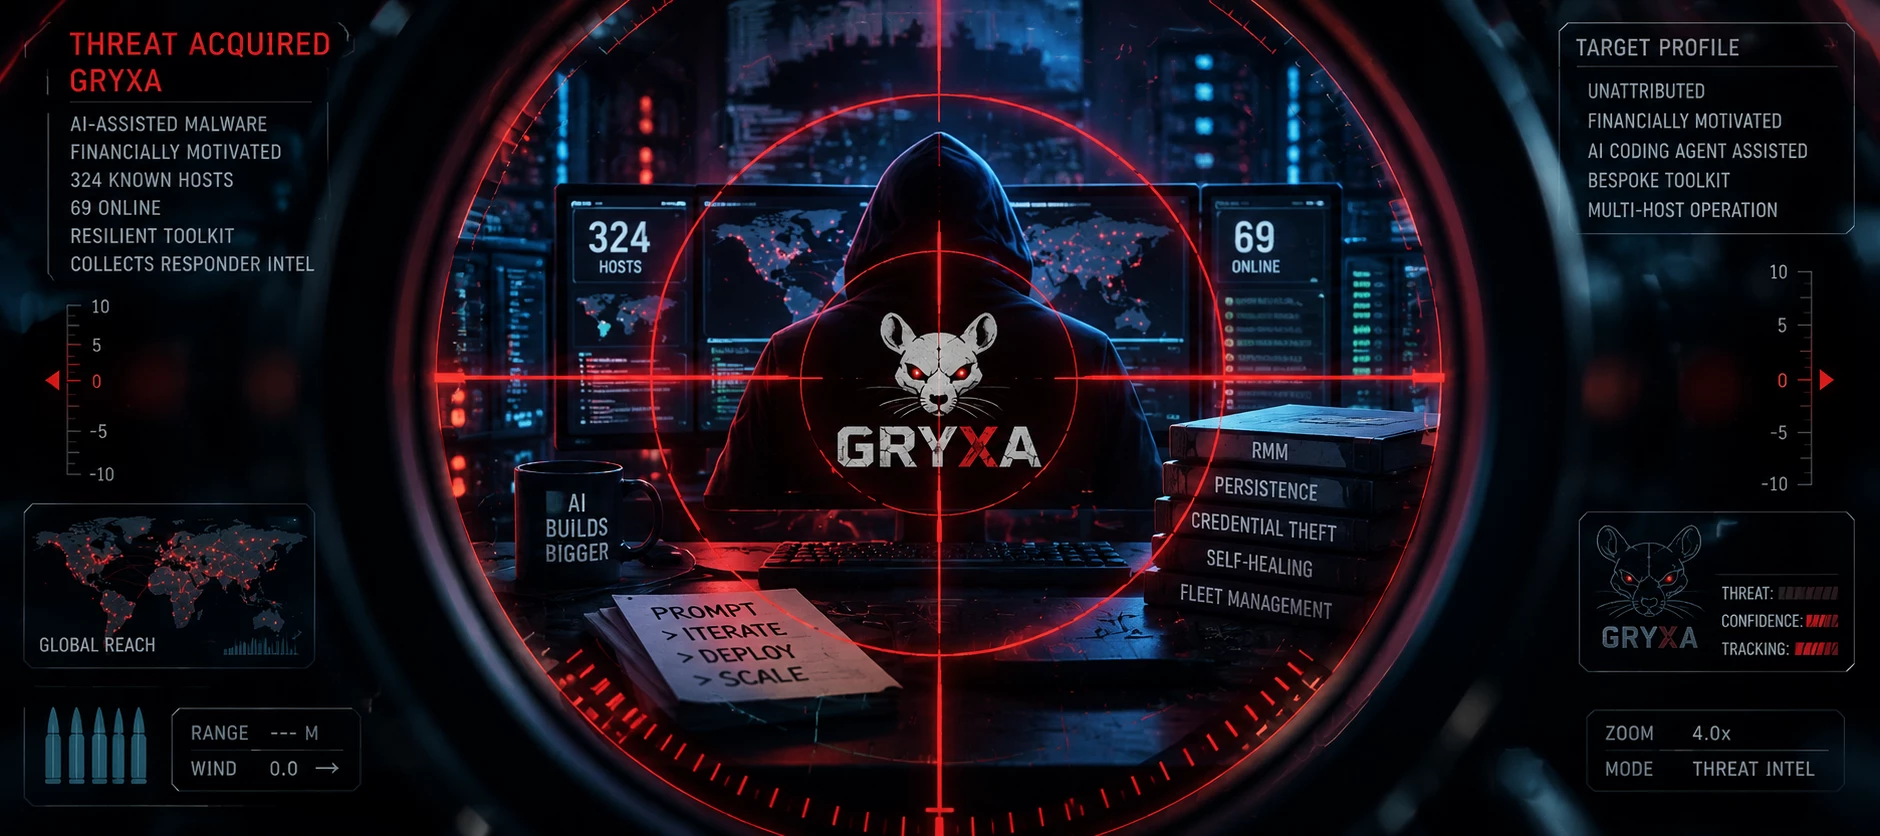
  Gryxa stages its RMM implant, guard, keeper and credential modules under a primary WinRTCS
  directory in ProgramData, two "keeper" directories chosen to blend in with Windows Error Reporting
  and Diagnosis paths (.wucache / .etlcache), and an off-path backup cache that the other components
  rebuild from. All four are marked hidden. Because the actor rotates component hashes through a
  signed update pipeline, these path and filename artifacts are a more durable indicator than file
  hashes. Also catches attrib +h/+s being applied to these paths during install.
reference:
  - https://reliaquest.com/blog/threat-spotlight-gryxa-ai-built-toolkit/
  - https://cybersecuritynews.com/new-ai-built-malware-watches/
  - https://radar.offseq.com/threat/toolkit-ai-assisted-development-and-persistent-threat-operations-194c32b91cc7dc2b
labels:
  - attack.defense_evasion
  - attack.persistence
  - attack.t1036.005
  - attack.t1564.001
  - Gryxa
  - RMM Abuse
  - AI-Assisted Malware
logsource:
  category: process_creation
  product: windows
detection:
  selection_gryxa_paths:
    - Image|contains:
        - '\ProgramData\WinRTCS\'
        - '\ProgramData\Microsoft\WinRTCS\'
        - '\WER\Temp\.wucache'
        - '\Diagnosis\State\.etlcache'
    - ChildProcessCommandLine|contains:
        - '\ProgramData\WinRTCS'
        - '\ProgramData\Microsoft\WinRTCS'
        - '\WER\Temp\.wucache'
        - '\Diagnosis\State\.etlcache'
    - ParentImage|contains:
        - '\ProgramData\WinRTCS\'
        - '\ProgramData\Microsoft\WinRTCS\'
        - '\WER\Temp\.wucache'
        - '\Diagnosis\State\.etlcache'
  selection_gryxa_scripts:
    ChildProcessCommandLine|contains:
      - 'own_lib.ps1'
      - 'own_mon.cmd'
      - 'SESSION_HANDOFF.md'
  selection_hide_attrib:
    Image|endswith: '\attrib.exe'
    ChildProcessCommandLine|contains: '+h'
    ChildProcessCommandLine|contains:
      - '\ProgramData\WinRTCS'
      - '\WER\Temp\.'
      - '\Diagnosis\State\.'
      - '\ProgramData\Microsoft\WinRTCS'
  condition: 1 of selection_*
criticality: High
saveasthreat: false

violation_summary:
  grouping_attribute: 'AccountName'
  level2_attribute: 'DeviceHostName'
  level2_metadata_attributes:
  metadata_attributes:
TECHNICAL DETAILS
Gryxa on-disk layout (ReliaQuest, Aug 2026):
C:\ProgramData\WinRTCS (primary)
C:\ProgramData\Microsoft\Windows\WER\Temp\.wucache (keeper)
C:\ProgramData\Microsoft\Diagnosis\State\.etlcache (keeper)
C:\ProgramData\Microsoft\WinRTCS\cache\ (off-path file copy, rebuild source)
Component scripts named in the actor repo:
own_lib.ps1 - per-host identity, WMI watchdog, service repair for persistence layer
own_mon.cmd - monitoring component that pins the fleet update channel
Both carry a false "Authorized internal deployment - lab/competition scope only" header.
No legitimate Microsoft component writes dot-prefixed cache directories under WER\Temp or
Diagnosis\State. WinRTCS is not a Microsoft product name.
False positives: none expected. Any hit should be treated as confirmed Gryxa presence.
Containment order matters - block actor infrastructure at the edge BEFORE touching the
host, otherwise the guard component escalates against endpoint protection (see EDR-SYM966).
Policy building walkthrough can be found in this previous post: