name: Scheduled Task Registered with Sub-Hourly Repetition Executing from ProgramData or Diagnostics Path Analytic
signatureid: WEL-ACC82-RUN
category: 'Persistence'
threatname: 'Scheduled Task/Job: Scheduled Task'
functionality: 'Microsoft Windows'

description: |
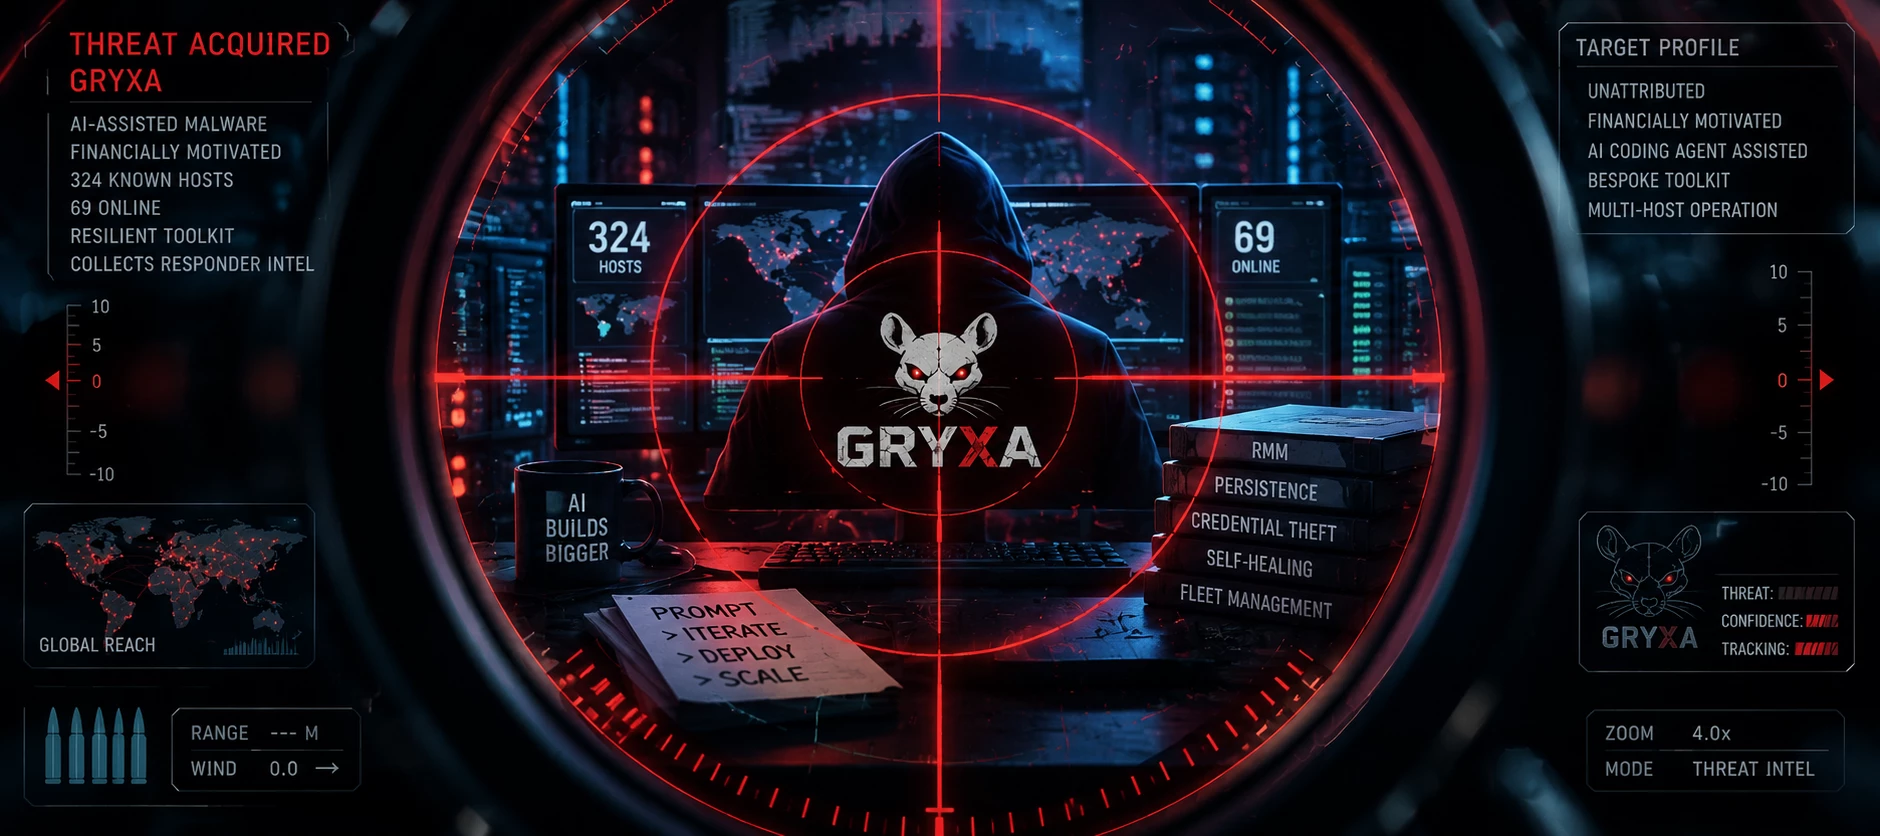
  Detects Windows Security event 4698 (scheduled task created) where the task XML defines a
  repetition interval of 1, 5 or 15 minutes, or a boot/logon trigger, and the action executes from
  ProgramData, Windows Error Reporting or Diagnosis paths. This is the Security-log view of the
  Gryxa persistence layer and catches task registration performed through the Task Scheduler COM
  API or PowerShell Register-ScheduledTask, which do not spawn schtasks.exe and are therefore
  invisible to process-creation rules. Gryxa's seven-task persistence set runs as SYSTEM on
  one-, five- and fifteen-minute intervals with additional onstart and onlogon triggers.
reference:
  - https://reliaquest.com/blog/threat-spotlight-gryxa-ai-built-toolkit/
  - https://cybersecuritynews.com/new-ai-built-malware-watches/
labels:
  - attack.persistence
  - attack.t1053.005
  - Gryxa
  - RMM Abuse
logsource:
  product: Windows
  service: Security
detection:
  selection_task_created:
    BaseEventId: 4698
  selection_interval:
    TaskContent|contains:
      - '<Interval>PT1M</Interval>'
      - '<Interval>PT5M</Interval>'
      - '<Interval>PT15M</Interval>'
      - '<BootTrigger>'
      - '<LogonTrigger>'
  selection_action_path:
    TaskContent|contains:
      - '\ProgramData\WinRTCS'
      - '\ProgramData\Microsoft\WinRTCS'
      - '\WER\Temp\.'
      - '\Diagnosis\State\.'
      - '\ProgramData\'
      - '\Users\Public\'
      - '\AppData\Local\Temp\'
  selection_system_principal:
    TaskContent|contains:
      - '<UserId>S-1-5-18</UserId>'
      - '<UserId>SYSTEM</UserId>'
      - '<UserId>NT AUTHORITY\SYSTEM</UserId>'
  filter_known_vendor_paths:
    TaskContent|contains:
      - '\ProgramData\Microsoft\Windows Defender\'
      - '\ProgramData\Microsoft\Windows\WER\ReportQueue\'
      - '\ProgramData\Dell\'
      - '\ProgramData\Lenovo\'
      - '\ProgramData\HP\'
      - '\ProgramData\Adobe\'
      - '\ProgramData\Google\'
      - '\ProgramData\Mozilla\'
      - '\ProgramData\Package Cache\'
  condition: selection_task_created and selection_interval and selection_action_path and selection_system_principal and not filter_known_vendor_paths
criticality: High
saveasthreat: false

violation_summary:
  grouping_attribute: 'DeviceHostName'
  level2_attribute: 'AccountName'
  level2_metadata_attributes:
  metadata_attributes:
TECHNICAL DETAILS
Requires audit policy "Object Access > Audit Other Object Access Events" (Success) for 4698.
Field mapping (Microsoft Windows functionality): customstring1 = TaskName, TaskContent = TaskContent (task XML).
Task XML fragments to expect from Gryxa:
<Triggers><TimeTrigger>...<Repetition><Interval>PT1M</Interval>...
<Principal><UserId>S-1-5-18</UserId><RunLevel>HighestAvailable</RunLevel>
<Actions><Exec><Command>powershell.exe</Command><Arguments>... C:\ProgramData\WinRTCS\...
False positives: Vendor agents that self-schedule sub-hourly SYSTEM tasks under ProgramData.
Add them to filter_known_vendor_paths.
Policy building walkthrough can be found in this previous post: