name: SYSTEM Scheduled Task Created with Minute Interval Executing from ProgramData or Diagnostics Path Analytic
signatureid: EDR-SYM965-RUN
category: 'Persistence'
threatname: 'Scheduled Task/Job: Scheduled Task'
functionality: 'Endpoint Management Systems'

description: |
  Detects schtasks.exe creating a task that runs as SYSTEM on a short minute-based repetition
  interval (1, 5 or 15 minutes) where the task action executes a script or binary from ProgramData,
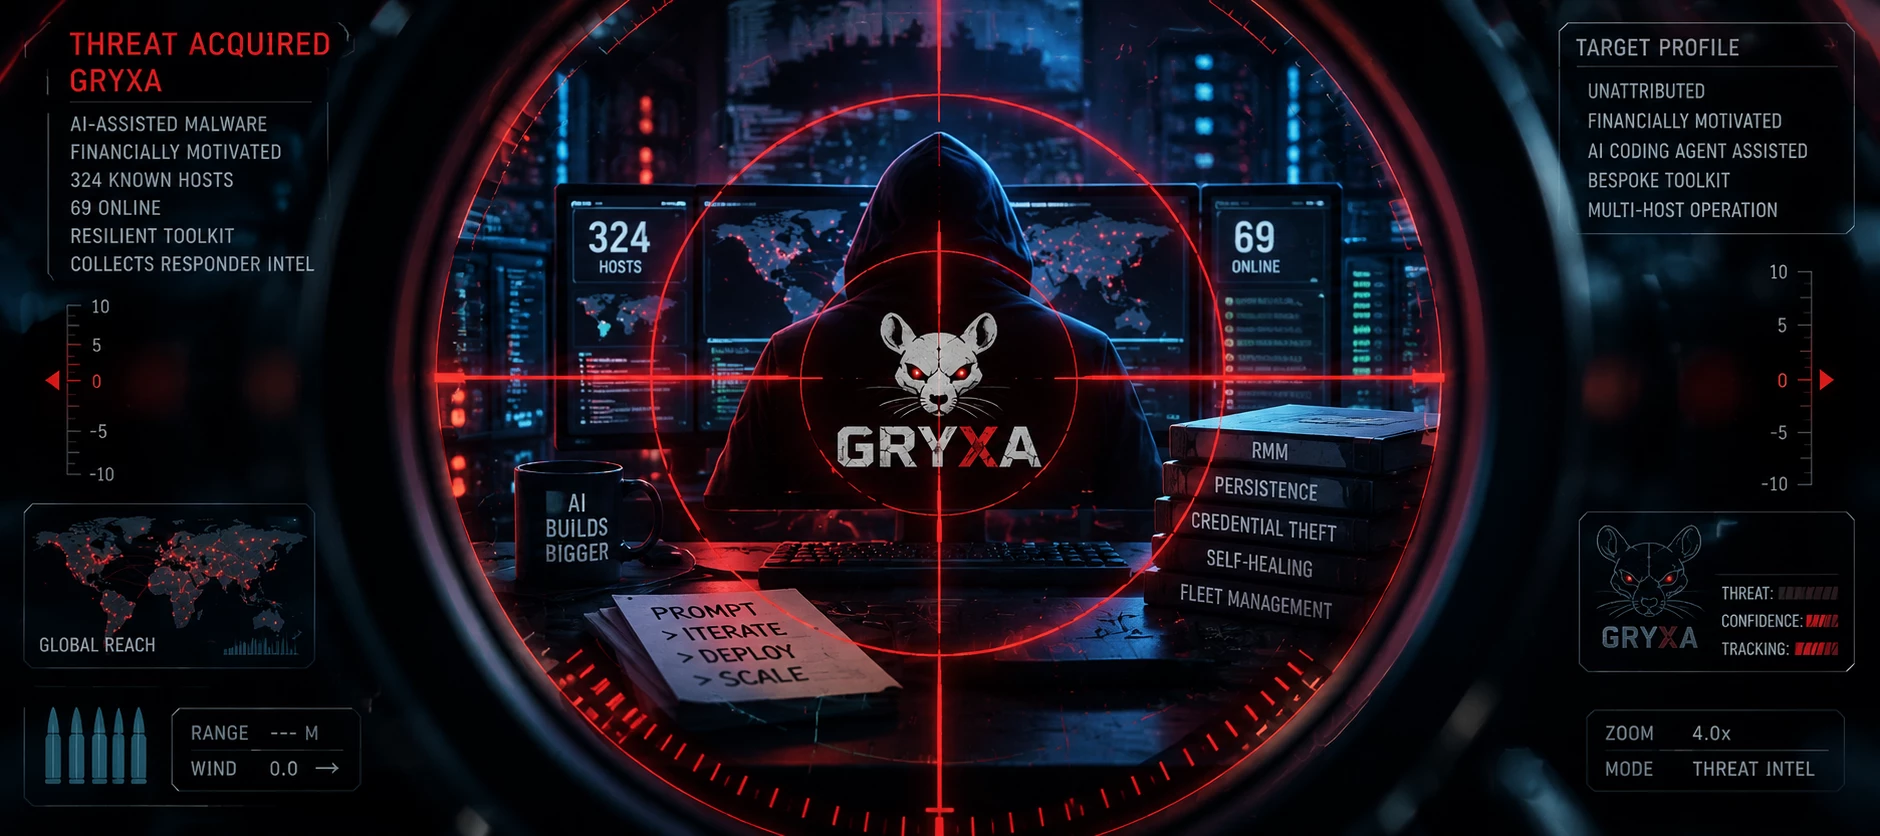
  Windows Error Reporting, or Diagnosis paths. Gryxa registers three WinRTCS tasks as SYSTEM at
  one-, five- and fifteen-minute intervals, each of which re-creates the full task set if any task
  is deleted. A further four "keeper" tasks use names resembling legitimate Microsoft tasks, two on
  one-minute intervals and one each at system start and user logon. The combination of SYSTEM
  principal, sub-hourly interval and a non-Program Files action path is rare in legitimate
  administration.
reference:
  - https://reliaquest.com/blog/threat-spotlight-gryxa-ai-built-toolkit/
  - https://cybersecuritynews.com/new-ai-built-malware-watches/
labels:
  - attack.persistence
  - attack.privilege_escalation
  - attack.t1053.005
  - Gryxa
  - RMM Abuse
logsource:
  category: process_creation
  product: windows
detection:
  selection_schtasks_create:
    Image|endswith: '\schtasks.exe'
    ChildProcessCommandLine|contains: '/create'
  selection_system_principal:
    ChildProcessCommandLine|contains:
      - '/ru system'
      - '/ru "system"'
      - '/ru nt authority\system'
      - '/ru "nt authority\system"'
      - '/ru "NT AUTHORITY\SYSTEM"'
      - '/ru S-1-5-18'
  selection_minute_interval:
    ChildProcessCommandLine|contains: '/sc minute'
    ChildProcessCommandLine|contains:
      - '/mo 1 '
      - '/mo 1"'
      - '/mo 5 '
      - '/mo 5"'
      - '/mo 15 '
      - '/mo 15"'
  selection_boot_logon:
    ChildProcessCommandLine|contains:
      - '/sc onstart'
      - '/sc onlogon'
  selection_action_path:
    ChildProcessCommandLine|contains:
      - '\ProgramData\'
      - '\WER\Temp\'
      - '\Diagnosis\State\'
      - '\AppData\Local\Temp\'
      - '\Users\Public\'
  filter_known_vendor_paths:
    ChildProcessCommandLine|contains:
      - '\ProgramData\Microsoft\Windows Defender\'
      - '\ProgramData\Microsoft\Windows\WER\ReportQueue\'
      - '\ProgramData\Dell\'
      - '\ProgramData\Lenovo\'
      - '\ProgramData\HP\'
      - '\ProgramData\Adobe\'
      - '\ProgramData\Google\'
      - '\ProgramData\Mozilla\'
      - '\ProgramData\chocolatey\'
      - '\ProgramData\Package Cache\'
  condition: selection_schtasks_create and selection_system_principal and (selection_minute_interval or selection_boot_logon) and selection_action_path and not filter_known_vendor_paths
criticality: High
saveasthreat: false

violation_summary:
  grouping_attribute: 'DeviceHostName'
  level2_attribute: 'AccountName'
  level2_metadata_attributes:
  metadata_attributes:
TECHNICAL DETAILS
Gryxa persistence layer (7 tasks across 2 layers):
WinRTCS layer : 3 tasks, SYSTEM, /sc minute /mo 1 | /mo 5 | /mo 15 -> each re-creates the full set
Keeper layer : 4 tasks, Microsoft-lookalike names, 2x /mo 1, 1x onstart, 1x onlogon
Task names were not published; this rule is name-agnostic by design because the actor's
update pipeline can rename tasks fleet-wide in one commit.
Emulation command shape:
schtasks /create /tn "<name>" /sc minute /mo 1 /ru SYSTEM /f /tr "powershell -ep bypass -w hidden -f C:\ProgramData\WinRTCS\own_lib.ps1"
False positives: Some RMM/backup agents register SYSTEM tasks under ProgramData. Extend
filter_known_vendor_paths with approved vendors; do not remove the interval constraint.
Policy building walkthrough can be found in this previous post: